Yes — Access Dental Management LLC disclosed a cyber incident affecting hundreds of thousands of people across its dental service organization footprint. The Texas OAG published 341,039 affected Texans on November 13, 2026. BreachTally’s readout of filing BR-0005517 reports 455,888 individuals in total in that Texas record, with breach dates May 1–4, 2026 and a 193-day gap from the end of that window to the Texas listing.
This is a confirmed regulatory filing and a published company notice on accessdentalclinics.com — not a finished criminal attribution story. Access Dental’s PDF does not name ransomware, a leak site, or how the unauthorized actor got in.
We tabulated the filing in the November 13 Texas OAG week roundup. This post is the standalone DSO notice, timeline, phishing-risk, website-tech, blacklist, lookalike, CourtListener, and MFA write-up for accessdentalclinics.com — the Irving, Texas management company’s public web host — not unrelated domains such as accessdental.co.za.
Snapshot
| Field | Detail |
|---|---|
| Entity | Access Dental Management LLC (dba Access Dental & Orthodontics) |
| HQ / filing address | 3050 Regent Boulevard, Suite 110, Irving, TX 75063 |
| Official web host | accessdentalclinics.com |
| Texans affected (OAG) | 341,039 · published Nov 13, 2026 |
| Total in Texas AG readout | 455,888 individuals (BreachTally BR-0005517) |
| Vermont AG | 10 residents · reported Nov 12, 2026 (BreachTally) |
| Consumer notice (Texas) | Yes · U.S. Mail (Texas OAG) |
| Assistance line | 1-844-770-7442 (company notice PDF) |
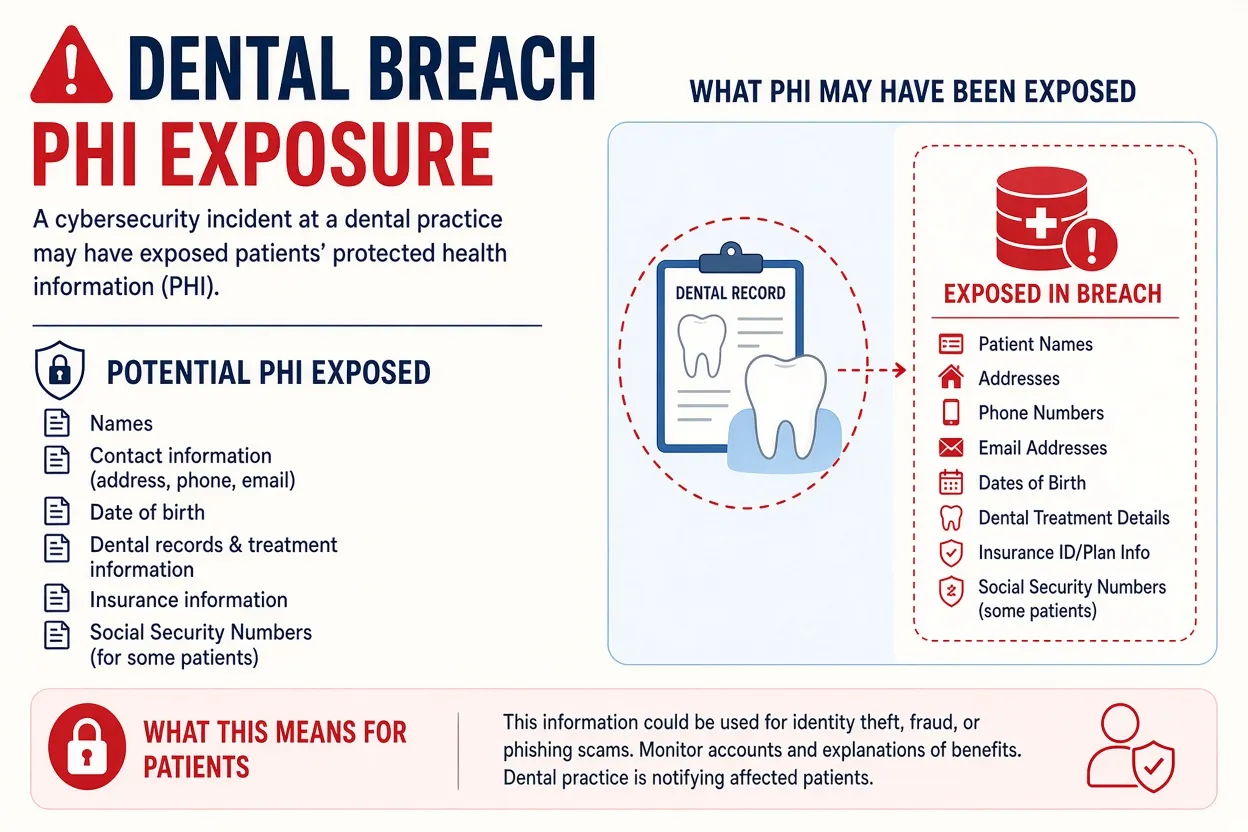
Data categories (Texas OAG)
Name, address, Social Security number, medical information, health insurance information, and date of birth — matching the company’s notice PDF.
What Access Dental says happened
Per the company notice PDF:
- May 1–4, 2026 — Unauthorized individual may have viewed and copied certain information.
- May 5, 2026 — Access Dental became aware of unusual activity and began investigation with counsel and forensic specialists.
- October 21, 2026 — Review of potentially impacted information finished.
- Notice letters mailed to individuals with valid addresses; PDF posted on the official website.
The PDF does not describe initial access method, malware family, or whether data was encrypted at rest.
Dates — compare sources before you quote one timeline
| Source | Key dates | Notes |
|---|---|---|
| Company PDF | Activity May 1–4; aware May 5; review done Oct 21 | Primary resident-facing notice |
| BreachTally BR-0005517 | Window May 1–4; discovered Oct 21 in AG metadata | 193 days from window end to Texas record Nov 13 |
| Texas OAG portal | 341,039 Texans · Nov 13, 2026 | Structured count and notice method — not full narrative |
| SecurityWeek (Nov 17, 2026) | Cites 341,049 (TX + VT split) | Secondary trade press |
We do not merge “became aware May 5” with BreachTally’s Oct 21 discovery field into one label. The May 5 date is awareness of unusual activity; Oct 21 is when the data review completed per the company PDF — BreachTally’s Texas record aligns with that completion date for statutory timing math.
WorldLeaks (World Leaks) ransomware / extortion claim (unverified): SecurityWeek and Becker’s Dental Review cite third-party reporting that a threat actor claimed responsibility on June 5, 2026. Access Dental has not confirmed that claim in the PDF we reviewed. Treat leak-site posts as unverified unless the organization or a regulator corroborates them.
Why Texas dental DSO domains matter after a delayed mail notice
DSOs centralize patient scheduling, insurance, and corporate mail while clinics keep local phone numbers. When SSNs plus medical and insurance fields hit a Texas OAG row months after May activity, the practical risk is fake “enrollment” or “credit monitoring” mail and omission domains that look like “Access Dental Clinics” without the final s.
Type accessdentalclinics.com yourself. The homepage lists multi-state offices; the breach PDF lives under that host’s wp-content tree as of November 17, 2026.
Access Dental states it supports more than 25 practices across Texas, New Mexico, Indiana, and Illinois (Becker’s citing the company website). That scale amplifies lookalike and call-center impersonation risk during a paper-notice window.
MFA: YubiKey and Google Authenticator
Strong MFA on corporate admin and patient portals does not prove whether May files were copied. It does reduce credential phishing after a breach headline.
| Grade | Meaning |
|---|---|
| Fail | SMS, email OTP, phone call, or no published YubiKey / open TOTP |
| Pass | Self-serve Google Authenticator-style open TOTP |
| Strong | FIDO2 / YubiKey-class security key for sign-in |
| Platform | Grade | YubiKey | Authenticator |
|---|---|---|---|
| Public WordPress marketing / scheduling site | Fail | No public docs | No public docs |
| Dedicated assistance line only | Unevaluated | N/A | N/A |
We did not find public documentation on accessdentalclinics.com for staff or patients to enroll YubiKey or Google Authenticator on a login portal. The published consumer path is call 1-844-770-7442 with the mailed letter — appropriate for notice, but not a substitute for hardening admin email and practice-management accounts.
Directory: MFA support directory · filter Healthcare where applicable.
Recommended MFA tools (for practice staff and personal mail)
| Product | Best for | Get it |
|---|---|---|
| YubiKey 5C NFC | USB-C laptops + NFC phones | Amazon |
| YubiKey 5 NFC | USB-A desktops + NFC phones | Amazon |
| Proton Pass | Passkeys + authenticator-style TOTP | Proton Pass |
We may earn a commission if you buy a YubiKey or sign up for Proton Pass through the links above.
Independent cybersecurity audits (admin API)
We ran side-effect-free GET https://audit.emailmenow.com/api/admin/scan?scope=full on November 17, 2026 (admin-scan bearer pattern; no public /?domain= URL and no POST /start). 100% is the ideal overall domain-security score. 0 of 2 hosts reach it.
| Organization | Domain | Overall | Gap vs 100% |
|---|---|---|---|
| Access Dental (official) | accessdentalclinics.com | 40% | −60 |
| Omission lookalike | accessdentalclinic.com | 34% | −66 |
| Domain | Identity | Transport | Website |
|---|---|---|---|
| accessdentalclinics.com | 35% | 15% | 40% |
| accessdentalclinic.com | 25% | 15% | 37% |
How to read this: accessdentalclinics.com at 40% with 15% transport is the familiar MTA-STS enforcement gap — relevant when spoofed “breach monitoring” or “patient records” mail circulates after a paper notice. 35% identity leaves room for convincing @accessdentalclinics.com impersonation. accessdentalclinic.com (singular clinic) is a registered lookalike with its own MX — treat it as unverified unless Access Dental says they own it; its 25% identity is worse, not safer.
These scores measure public email authentication, transport policy, and website headers. They do not prove whether May 2026 files were copied.
DSOs and clinics should still run a baseline check on the free domain security scan landing page (search the domain on the homepage — do not trust emailed ?domain= links). For managed review after an incident, see EmailMeNow services.
Website stack
Passive website-tech probe on November 17, 2026 (node scripts/probe-website-tech.mjs accessdentalclinics.com --fresh --for-news):
| Domain | Stack signal |
|---|---|
| accessdentalclinics.com | Stack undetected (low fingerprint confidence) |
| TLS (CT) | Let’s Encrypt; expires 2026-12-31 (~43d at probe time) |
Point-in-time only — public WordPress marketing stack is not proof that practice-management or imaging systems match this footprint.
Blacklist and lookalikes
Email blacklist (public DoH, November 17, 2026): accessdentalclinics.com clear (0 mail/domain hits on checked lists). UCEPROTECT notes on a shared web IP are provider noise — not led here.
DNS lookalike scans on accessdentalclinics.com:
| Profile | To review | BEC staging | Note |
|---|---|---|---|
| Standard | 1 | 0 | accessdentalclinic.com — omission — registered (NS, A, MX) |
| BEC | 1 | 0 | Same omission candidate |
Patients and staff should treat accessdentalclinic.com (singular clinic) as unverified unless Access Dental explicitly says they own it. Continuous monitoring: Cybersquat Domain Monitoring.
CourtListener
CourtListener REST search on November 17, 2026 for Access Dental Management and data breach in Texas federal districts returned no HIPAA-style breach docket tied to the November 2026 AG filings.
A name match returned June 2026 diversity contract suits (Ramos and Diaz v. Access Dental Management Services LLC, W.D. Tex. 3:26-cv-01963 and 3:26-cv-01938) — other contract captions, not reviewed as breach class actions for this incident. Do not cite them as confirmation of the May network event.
What patients and practices should do now
- Read the official notice PDF. Call 1-844-770-7442 only with the mailed letter in hand — not because a text or email told you to.
- Watch explanation-of-benefits and credit reports for unfamiliar medical or financial activity — SSN plus insurance data supports medical identity theft and tailored phishing.
- Ignore links in unexpected “Access Dental monitoring” or “orthodontic records update” messages. Type
accessdentalclinics.comand use the PDF path from that host. - Practice owners: require FIDO/YubiKey or open TOTP on Microsoft 365 / practice-management admin roles; enforce DMARC reject and MTA-STS on the corporate domain before the next mail notice cycle.
- Report phishing to the FBI IC3 and the Texas Attorney General.
Related coverage
- Texas OAG breaches — week of Nov 13, 2026
- Healthcare AG breach tracker
- Texas healthcare breaches hub
- Texas OAG YTD dashboard
- Top Texas dental groups — email security listicle
Sources: Texas OAG Data Security Breach Reports · BreachTally BR-0005517 · Access Dental notice PDF · Access Dental Clinics homepage · Becker’s Dental Review (Nov 16, 2026) · SecurityWeek (Nov 17, 2026). Independent EmailMeNow admin-scan attempt, website-tech, blacklist, cybersquat, and CourtListener work November 17, 2026.