AngMar Management Services — a privately held home-health and hospice management company in Mansfield, Texas — told patients that an unauthorized actor may have accessed or acquired files on or around July 18, 2026. The company identified unusual network activity on July 20, finished its data review on September 8, and mailed notices dated September 22.
This is a confirmed company notice, not a rumor. The sample letter lists names, addresses, dates of birth, Social Security numbers, patient IDs, medical record numbers, insurance, dates of service, diagnosis or condition, providers, prescriptions, and medical history. HHS OCR later posted 126,196 individuals (September 16). The Texas Attorney General lists 35,916 Texans (published September 25).
HIPAA Journal and SecurityWeek report that the Interlock ransomware group added AngMar to a leak site in August 2026 and claimed about 710 GB. AngMar’s letter does not name a crew or confirm that volume. Treat the leak-site figure as a claim.
AngMar manages more than 90 locations in 11 states under brands including Angels Care Home Health. Headquarters on the public site: 2301 FM 1187, Suite 203, Mansfield, TX 76063. A separate July 2026 social-engineering notice from Clover Health is a different victim.
Snapshot
| Field | Detail |
|---|---|
| Company | AngMar Management Services (Mansfield, TX) |
| Access window | On or around July 18, 2026 (found July 20) |
| Individuals | OCR 126,196 · Texas OAG 35,916 |
| Actor | Interlock claimed ~710 GB; not named in the letter |
What AngMar told patients
The September 22 letter says AngMar hired outside forensics, secured systems, and has no evidence of misuse so far. It still offered 12 months of single-bureau credit monitoring through Cyberscout (a TransUnion company).
Help line: 1-877-520-9311, Monday–Friday 8 a.m.–8 p.m. ET. Mail: AngMar Management Services, c/o Cyberscout, PO Box 1286, Dearborn, MI 48120-9998. Company contact on the public site remains info@angmarms.com / 877-469-6739.
OCR lists AngMar as a business associate. HIPAA Journal also notes other state AG filings. Do not treat the Texas count as the nationwide total — OCR is larger.
Interlock claim — and the Texas lawsuits
Interlock’s August listing is allegation-led. We do not link leak sites or quote samples. The 2024 Interlock claim against Texas Tech University Health Sciences Center is a different victim and year.
CourtListener already has Northern District of Texas putative class actions against AngMar Medical Holdings, Inc.:
| Case | Docket | Filed |
|---|---|---|
| Lavern v. AngMar | 4:26-cv-00996 | Aug 13, 2026 |
| Bauer v. AngMar | 4:26-cv-00997 | Aug 13, 2026 |
| Kingsboro v. AngMar | 4:26-cv-01029 | Aug 19, 2026 |
Those RECAP rows are diversity / personal-injury filings. They are not a finding that Interlock’s 710 GB figure is true.
What patients and staff should do
- Type angmarms.com or use the number on your letter. Do not use a “records restored / Interlock portal” link from email or text.
- Enroll in Cyberscout only from the letter. The help line is 1-877-520-9311.
- Freeze credit and watch bank, Medicare, and insurance EOBs if you received Angels Care or another AngMar-managed service.
- Staff and referral partners: reset work passwords on a host you typed. Assume follow-on payroll and “your hospice file is online” phishing.
- Texas residents can confirm the OAG row at the Texas breach portal. Nationwide: IC3.
MFA: YubiKey and Google Authenticator
A hardware key does not un-copy files that already left the network. It does cut a lot of the follow-on “verify your chart / Cyberscout / W-2” phishing that follows a hospice headline. Grades match our MFA directory.
| Grade | Meaning |
|---|---|
| Fail | SMS, voice, or email OTP — or no public path |
| Pass | Self-serve Google Authenticator-style open TOTP |
| Strong | FIDO2 / YubiKey-class security key for sign-in |
| Platform | Grade | YubiKey | Authenticator |
|---|---|---|---|
| AngMar / Angels Care | Fail | No | No |
| Texas OAG portal | Fail | No | No |
angmarms.com is a marketing site. It publishes no patient- or staff-portal MFA help that names a YubiKey or Google Authenticator. We do not invent an Angels Care MyChart tenant. MFA would not have recalled the July files; it still matters for the mail that comes next.
Directory: MFA support directory · Category → Healthcare.
Recommended MFA tools
| Product | Best for | Get it |
|---|---|---|
| YubiKey 5C NFC | USB-C laptops + NFC phones | Amazon |
| YubiKey 5 NFC | USB-A desktops + NFC phones | Amazon |
| Proton Pass | Passkeys + authenticator-style TOTP | Proton Pass |
We may earn a commission if you buy a YubiKey or sign up for Proton Pass through the links above.
Independent cybersecurity audits
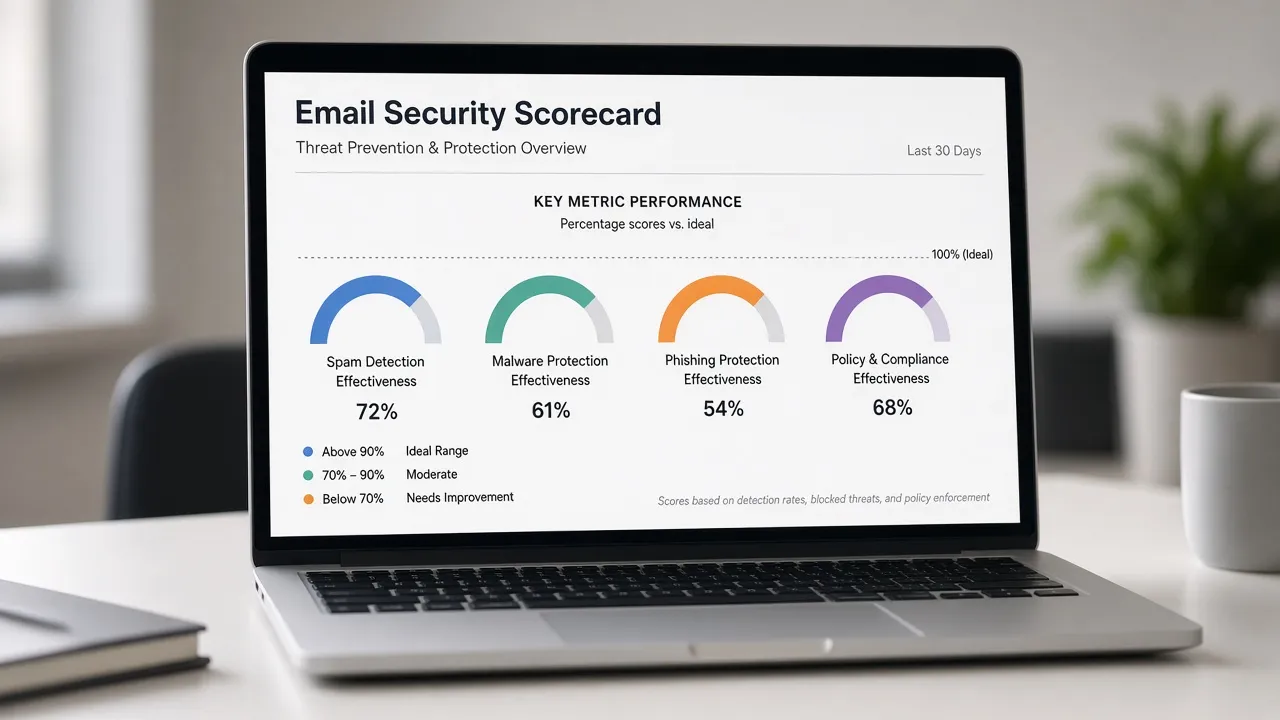
We audited the official AngMar host, a shorter brand host, HIPAA Journal, and the Texas OAG on October 11, 2026. 100% is the ideal — none reach it. These scores are public email / transport / website posture. They do not say how the July files were reached.
| Organization | Domain | Overall | vs 100% |
|---|---|---|---|
| HIPAA Journal | hipaajournal.com | 56% | −44 |
| AngMar (official) | angmarms.com | 47% | −53 |
| Texas OAG | texasattorneygeneral.gov | 37% | −63 |
| AngMar (short) | angmar.com | 32% | −68 |
| Domain | Identity | Transport | Website |
|---|---|---|---|
| hipaajournal.com | 35% | 15% | 70% |
| angmarms.com | 35% | 15% | 40% |
| texasattorneygeneral.gov | 10% | 15% | 40% |
| angmar.com | 0% | 15% | 37% |
Audit links: angmarms.com · angmar.com · hipaajournal.com · texasattorneygeneral.gov
angmar.com Identity 0% is the spoofing risk: a fake “Cyberscout enrollment / Interlock takedown” message is easier to deliver than the overall 32% suggests. Type angmarms.com. Transport 15% on all four hosts means inbound mail can still be downgraded without MTA-STS enforce.
Website stack note
Passive website-tech probes on October 11, 2026:
| Domain | Stack signal |
|---|---|
| angmarms.com | Wix (hosted); Let’s Encrypt TLS expires 2026-12-06 |
| angmar.com | Stack undetected; HTTP→HTTPS redirect not confirmed |
| hipaajournal.com | Stack undetected; Let’s Encrypt TLS expires 2027-01-02 |
| texasattorneygeneral.gov | Stack undetected; Sectigo TLS expires 2026-12-09 |
Point-in-time only. A live marketing homepage is not a forensic finding on the copied files.
Blacklist and lookalike domains
Email blacklist checks (public DoH, October 11, 2026): angmarms.com, hipaajournal.com, and texasattorneygeneral.gov were clear on mail/domain lists we can query. angmar.com showed UCEPROTECT Level 3 plus SPFBL on a shared MX — low-signal provider-netblock noise, not proof the company is “blacklisted.” Wix and OAG web/CDN SPFBL notes are informational only.
DNS lookalike scans (BEC profile, registered signals only):
| Brand scanned | To review | Likely owned | BEC staging |
|---|---|---|---|
| angmarms.com | 1 | 0 | 0 |
| angmar.com | 8 | 0 | 0 |
| hipaajournal.com | 1 | 0 | 0 |
| texasattorneygeneral.gov | 1 | 1 | 0 |
High-interest registered names (investigate; not proof this incident used them):
| Lookalike | Technique | Note |
|---|---|---|
| angimarms.com | insertion | Live NS + A + MX |
| angmar.net / .org / .dev | tld-swap | Live DNS on the short brand |
| hipaajournal.co | tld-swap | Live NS + A + MX |
| texasattorneygeneral.org | tld-swap | Live NS + A + MX |
texasattorneygeneral.com redirected to the real .gov host when we checked. Type angmarms.com, not a one-letter swap. Continuous monitoring: Cybersquat Domain Monitoring.
Related coverage
- Clover Health social engineering / HHS 138,677 (same-week SecurityWeek pair; different victim)
- Texas Tech HSC / Interlock 2024 event
- HHS OCR week of Sep 16
- Texas OAG week of Sep 25
- Texas healthcare breaches 2026
- Nutex Health / The Gentlemen claim
- MFA support directory
Run a free audit at audit.emailmenow.com or contact EmailMeNow for healthcare DMARC / MTA-STS and phishing response aimed at the 100% ideal.