On Monday, November 16, 2026, customers reported difficulty with online and mobile banking at several large U.S. institutions. Downdetector user reports surged for Chase, Bank of America, Wells Fargo, U.S. Bank, Zelle, and others — but spikes on Downdetector are not a confirmed outage count and do not establish a cause.
A post on X by Matt Van Swol (~12:55 PM CT, Nov 16) shared a Downdetector-style board naming Chase, Bank of America, Zelle, U.S. Bank, Wells Fargo, JPMorgan, Truist, Capital One, plus Microsoft, Google/Gmail, and other consumer services. Treat that post as an unverified social claim until primary sources confirm each name.
Illustration — EmailMeNow. Not a bank logo or live status indicator.
Snapshot
| Field | Detail |
|---|---|
| Date checked | November 16, 2026 (America/Chicago) |
| Banks named in reporting | Chase, Bank of America, Wells Fargo, U.S. Bank, Zelle, JPMorgan, Truist, Capital One (plus others on Downdetector only) |
| Primary confirmation | Chase — technical issue; not cyber-related (Gizmodo) |
| Aggregator signal | Downdetector user reports — unverified volume |
| Social lead | @mattvanswol X post — unverified |
| Payment rail context | Plaid — Chase downtime affecting connections; U.S. Bank — Zelle cross-bank delays (Gizmodo) |
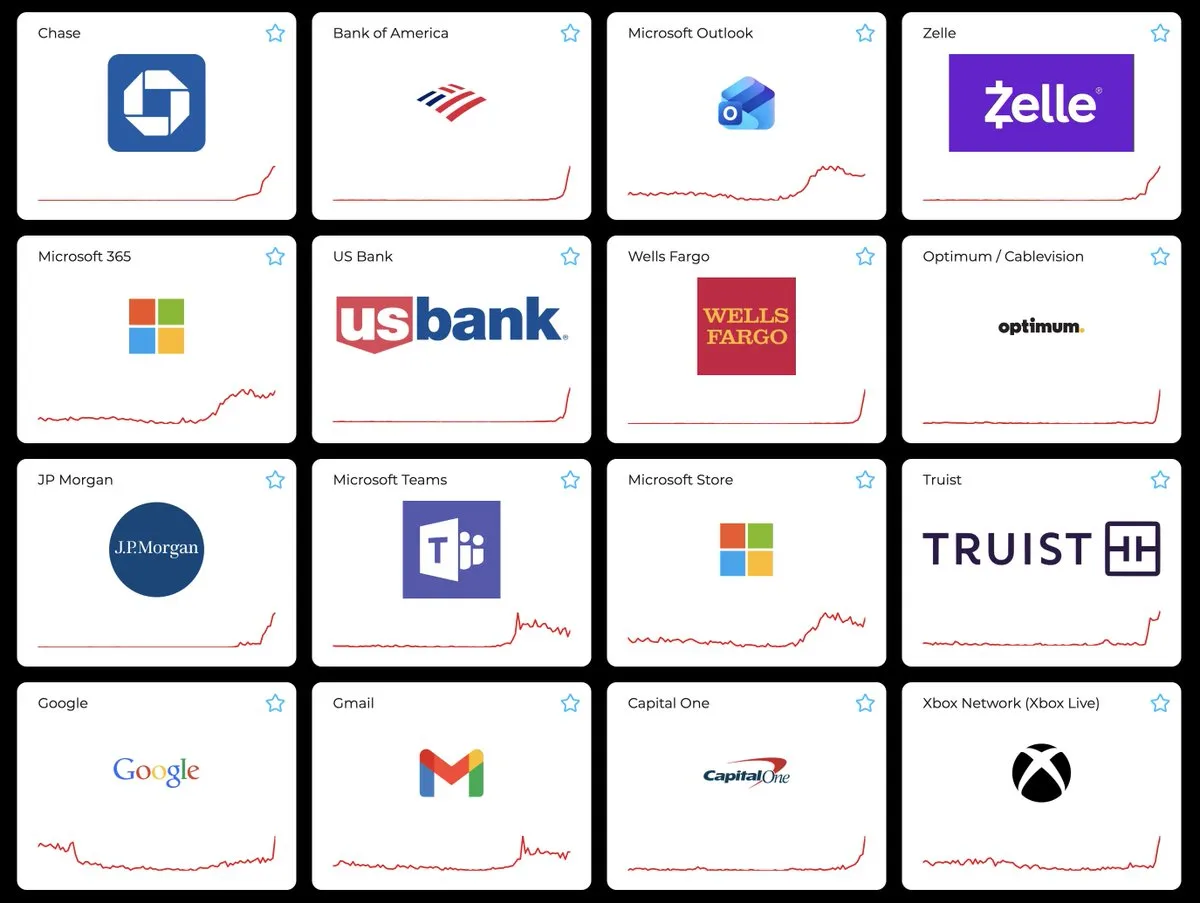
Screenshot via @mattvanswol on X (Nov 16, 2026). User-reported tiles, not an official bank or vendor status board.
What’s verified vs. unverified
Verified (primary or firsthand reporting)
| Fact | Source |
|---|---|
| Chase said a technical issue is making some transactions take longer than usual, while customers still have access to accounts and funds, and that Chase is working to resolve it quickly | Gizmodo (quotes Chase spokesperson, Nov 16, 2026); same wording carried by News 12 and trade press quoting Associated Press |
| Chase told Gizmodo the disturbances were “not cyber related” | Gizmodo |
| U.S. Bank said its systems are not directly impacted, but clients sending or receiving Zelle with another institution may see delays | Gizmodo |
| Plaid reported “Service Disruption Impacting Chase connections” — Chase downtime affecting item adds and API calls | Plaid Status (live status page at probe time) |
| Associated Press reported customers had difficulty accessing online accounts at major banks including Bank of America, Chase, U.S. Bank, Wells Fargo, and Zelle (headline also references Truist) | AP News, Nov 16, 2026 |
| Microsoft 365 business status page showed no active service-wide incident at probe time; the Nov 12–14, 2026 global Microsoft 365 disruption was remediated per Microsoft/AP | Microsoft 365 status · AP on restoration |
Unverified or user-report only
| Claim | Why it stays unverified |
|---|---|
| Matt Van Swol’s Downdetector board (banks + Microsoft/Google/others at once) | Social post — not a bank or vendor incident record |
| Downdetector spike heights (e.g., thousands of Chase reports) | User-submitted reports; not customer counts from institutions |
| Whether Bank of America, Wells Fargo, Truist, or Capital One had institution-wide outages | Gizmodo noted no immediate response from BoA/Wells at publish time; we found no matching official root-cause statement for those brands in primary sources used here |
| Shared upstream cause across banks and Microsoft/Google | Not established — Microsoft status was operational Nov 16; simultaneous Downdetector tiles alone do not prove a single root cause |
| Cyberattack / hack at any named bank | Not claimed by Chase’s verified statements; do not infer from Downdetector or social posts |
Do not train staff or customers that a named bank was hacked based on this traffic.
Banks in scope for this post
We audited the primary marketing / consumer domains below — the same names Matt Van Swol’s tile board highlighted. JPMorgan Chase retail login lives on chase.com; jpmorgan.com is the corporate site (also on the board).
| Institution | Primary domain audited |
|---|---|
| Chase (JPMorgan Chase) | chase.com |
| Bank of America | bankofamerica.com |
| Zelle | zellepay.com |
| U.S. Bank | usbank.com |
| Wells Fargo | wellsfargo.com |
| JPMorgan | jpmorgan.com |
| Truist | truist.com |
| Capital One | capitalone.com |
Independent domain audits (ideal 100%)
Fresh overall scores from audit.emailmenow.com on November 16, 2026. 100% is the ideal; none of these eight domains reached it in this pass.
| Bank | Domain | Overall | Website |
|---|---|---|---|
| Truist | truist.com | 85% | 95% |
| Zelle | zellepay.com | 81% | 95% |
| Chase | chase.com | 79% | 94% |
| JPMorgan | jpmorgan.com | 79% | 95% |
| U.S. Bank | usbank.com | 77% | 68% |
| Wells Fargo | wellsfargo.com | 67% | 87% |
| Bank of America | bankofamerica.com | 53% | 37% |
| Capital One | capitalone.com | 58% | 43% |
Identity / transport scores from the same audit pass (transport reflects MTA-STS/TLS reporting among other controls):
| Domain | Identity | Transport |
|---|---|---|
| truist.com | 90% | 15% |
| usbank.com | 90% | 15% |
| zellepay.com | 75% | 45% |
| bankofamerica.com | 50% | 45% |
| chase.com | 75% | 15% |
| jpmorgan.com | 75% | 15% |
| wellsfargo.com | 50% | 15% |
| capitalone.com | 60% | 15% |
These scores measure public email and website posture, not whether mobile login works today.
Email authentication (live DNS, Nov 16, 2026 CT)
| Domain | SPF (apex) | DMARC policy | DKIM (s1 selector) |
|---|---|---|---|
| chase.com | v=spf1 … -all | p=reject, pct=100, rua present | Not at s1 (common selector probe) |
| bankofamerica.com | v=spf1 … ~all | p=reject, rua/ruf present | Not at s1 |
| zellepay.com | v=spf1 … -all | p=reject, rua/ruf present | Not at s1 |
| usbank.com | v=spf1 … -all | p=reject, rua/ruf present | s1 public key present |
| wellsfargo.com | v=spf1 … ~all | p=reject (via Proofpoint CNAME), rua present | Not at s1 |
| jpmorgan.com | v=spf1 … -all | p=reject, pct=100, rua present | Not at s1 |
| truist.com | v=spf1 include:guard.truist.com -all | p=reject (Proofpoint-hosted) | s1 via SendGrid CNAME |
| capitalone.com | v=spf1 … ~all | p=reject (Agari CNAME) | s1 via SendGrid CNAME |
| Domain | MTA-STS DNS | Published policy | TLS-RPT | BIMI |
|---|---|---|---|---|
| chase.com | v=spf1 -all sentinel at _mta-sts | No reachable mta-sts policy file | Sentinel v=spf1 -all | VMC record present |
| bankofamerica.com | None at _mta-sts | None | None | VMC record present |
| zellepay.com | None | None | None | Zelle-hosted SVG + cert |
| usbank.com | None | None | None | None found |
| wellsfargo.com | None | None | None | VMC record present |
| jpmorgan.com | v=spf1 -all sentinel | None | Sentinel | VMC record present |
| truist.com | None | None | None | None found |
| capitalone.com | None | None | None | Capital One PEM/SVG |
TLS (openssl to :443, Nov 16, 2026): all eight domains negotiated TLS 1.3 in our probe (TLS 1.2 also available).
Website headers (HTTPS homepage, Nov 16, 2026 CT)
| Domain | HSTS | CSP / frame control | Other |
|---|---|---|---|
| chase.com | max-age=31536000 | CSP frame-ancestors 'none'; XFO SAMEORIGIN | Permissions-Policy present |
| bankofamerica.com | max-age=31536000; includeSubDomains | Strong default-src CSP; XFO SAMEORIGIN | — |
| zellepay.com | max-age=31536000; includeSubDomains; preload | Long CSP; frame-ancestors 'self' | Referrer-Policy on response |
| usbank.com | max-age=31536000 (homepage GET) | Broad default-src CSP | XCTO nosniff; referrer-policy no-referrer-when-downgrade |
| wellsfargo.com | max-age=31536000; includeSubDomains | Nonce-based CSP; XFO SAMEORIGIN | XCTO nosniff |
| jpmorgan.com | max-age=15768000; includeSubDomains; preload | CSP frame-ancestors 'self'; XFO SAMEORIGIN | XCTO nosniff |
| truist.com | max-age=63072000; includeSubdomains | CSP frame-ancestors lists Truist domains | XCTO nosniff |
| capitalone.com | max-age=31536000 | XFO SAMEORIGIN; referrer-policy strict-origin-when-cross-origin | XCTO nosniff |
hstspreload.org API returned unknown eligibility for each apex at probe time (not the same as “no HSTS header”).
Website stack note
Passive website-tech probes on November 16, 2026 (run-probe-domains-once.mjs) for all eight domains. One notable flag:
| Domain | Stack signal |
|---|---|
| zellepay.com | Drupal 11 behind current (latest 11.4.12 per probe) |
Stack signals describe the marketing site, not core banking uptime.
Outage-themed phishing — practical defenses
When login apps fail, criminals send “restore access”, “verify your account”, or “outage refund” texts and emails with lookalike links.
| Do | Don’t |
|---|---|
| Open the official app from your home screen or type the URL yourself | Click login links in unexpected email or SMS during an outage |
| Call the number on the back of your card | Trust caller ID or the phone number in a panic message |
| Check DMARC/SPF alignment on anything claiming to be your bank (failures are a red flag) | Share OTPs or approve MFA prompts you did not start |
| Wait for statements on official bank sites or verified news citing bank spokespeople | Assume Downdetector or a viral X post is a breach notice |
Illustration — EmailMeNow.
Strong DMARC reject on several of these domains helps receivers discard crude spoofs — but lookalike domains still land in inboxes. See cybersquat counts below.
Online banking MFA (YubiKey & authenticator apps)
Outage frustration does not change SIM-swap risk on SMS OTP. Grades follow our national banks MFA scorecard rules.
| Bank | Domain | YubiKey / FIDO | Open TOTP | Passkeys | Grade |
|---|---|---|---|---|---|
| Bank of America | bankofamerica.com | Yes | No | No | Strong |
| Chase | chase.com | No | No | Yes | Fail |
| U.S. Bank | usbank.com | No | No | Yes | Fail |
| Wells Fargo | wellsfargo.com | No | No | Yes | Fail |
| Capital One | capitalone.com | No | No | Yes | Fail |
| Truist | truist.com | No | No | Yes | Fail |
| JPMorgan (corporate) | jpmorgan.com | No | No | Yes (Chase docs) | Fail |
| Zelle network | zellepay.com | — | — | — | N/A (enroll through your bank’s app) |
Blacklist, lookalikes, and CourtListener
Email blacklist (public DoH, Nov 16, 2026): bankofamerica.com, zellepay.com, usbank.com, wellsfargo.com, truist.com, and capitalone.com were clear on mail/domain lists we query. chase.com and jpmorgan.com showed UCEPROTECT Level 3 hits on shared Symantec/Messagelabs MX IPs — provider noise, not a dedicated outbound block.
Cybersquat scans (standard profile, registered signals):
| Domain scanned | To review | Likely owned | BEC staging |
|---|---|---|---|
| bankofamerica.com | 132 | 26 | 1 |
| capitalone.com | 100 | 11 | 0 |
| wellsfargo.com | 84 | 28 | 0 |
| chase.com | 73 | 0 | 1 |
| jpmorgan.com | 63 | 0 | 2 |
| usbank.com | 62 | 4 | 0 |
| truist.com | 75 | 0 | 0 |
| zellepay.com | 35 | 0 | 1 |
Continuous monitoring: Cybersquat Domain Monitoring.
CourtListener (RECAP API v4, Nov 16, 2026): Texas federal entity searches for JPMorgan Chase, Bank of America, Wells Fargo, and Zelle returned unrelated historical dockets, not filings about this outage. A national keyword search for "online banking" outage Chase returned no on-point docket for Nov 16, 2026. Absence of a filing does not disprove user-reported login trouble — it simply means no federal case caption matched this incident in our query.
Related coverage
- National banks MFA — YubiKey, TOTP, passkeys
- Major U.S. banks email security benchmark
- Chameleon SEO poisoning — fake bank logins in search results
- FaceTime bank scam — live OTP theft
Check your domain free at audit.emailmenow.com, add Domain Watch ($29/mo) for weekly mail-authentication drift checks, or see automated reports and monitoring.
Sources: Associated Press · Gizmodo · Plaid Status · News 12 — Chase statement · Asbury Park Press — Downdetector user reports · Matt Van Swol on X (unverified social claim) · Microsoft 365 status · AP — Microsoft 365 restoration. Independent EmailMeNow audits, dig/curl/openssl probes, website-tech, blacklist, cybersquat scans, and CourtListener RECAP November 16, 2026 (America/Chicago). Downdetector figures are user reports, not bank-confirmed counts.