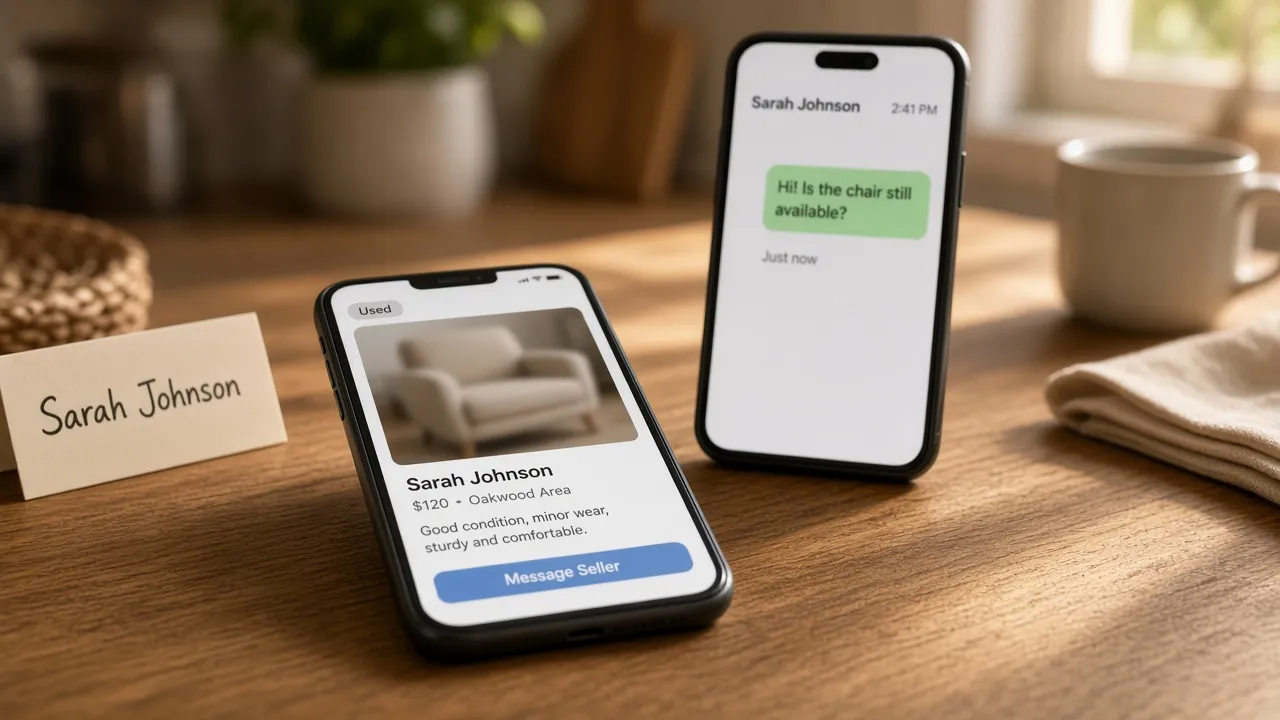
Malwarebytes reported October 6, 2026 that Facebook users are getting a text or iMessage that looks like a buyer asking about a Facebook Marketplace listing — and the attached picture names the recipient as the seller. The October 12 Malwarebytes newsletter put the same lure in the Byte-Sized Brief.
This is not a reported Facebook or Marketplace platform hack. A fabricated listing plus a matching name is a conversation lure. The useful prize for the sender is often a reply, which marks the number as live.
Type facebook.com or facebook.com/marketplace yourself. Do not reply to the text, tap the picture to “log in,” or send a one-time code.
Snapshot
| Field | Detail |
|---|---|
| Consumer alert | Malwarebytes — October 6, 2026 (newsletter October 12) |
| Channel | Unsolicited text / iMessage with a fake listing image |
| Platform breach | Not reported — fabricated listing, not a Marketplace outage |
| CourtListener | 0 RECAP dockets on this name-and-number lure (searched Oct 12, 2026) |
| Official hosts | Type facebook.com · facebook.com/hacked |
Who is at risk
Anyone whose name and mobile number travel together — a breach dump, a people-search list, or an old signup — can get this text. Malwarebytes notes that an AI agent plus a cheap name/number list makes the screenshot easy to stamp at scale. The profile photo in their sample belonged to another Facebook user with the same name. That is not proof your account was taken.
A reply does not “clear your name.” It tells the sender the number answers.
What to watch for
- “Is this still available for purchase?” (or close wording) from a number you do not know
- An attached Marketplace card that shows your name as the seller
- A profile photo that is not yours, even when the name matches
- A follow-up that asks you to tap, log in, call, scan a QR code, or share a code
- Off-platform payment or “Facebook support” after you engage — Meta’s Marketplace safety page flags early phone/email contact and off-platform login links
What to do
- Do not reply. Ignore the thread. A “that isn’t me” text is still a live-number ping.
- Open Facebook yourself. Check your listings, messages, logins, email, phone, and recovery settings. Use facebook.com/hacked only if you see real account abuse.
- If a real profile is impersonating you, save the URL and report it in Facebook. Do not use a link from the text.
- If money moved, keep records and file at IC3.
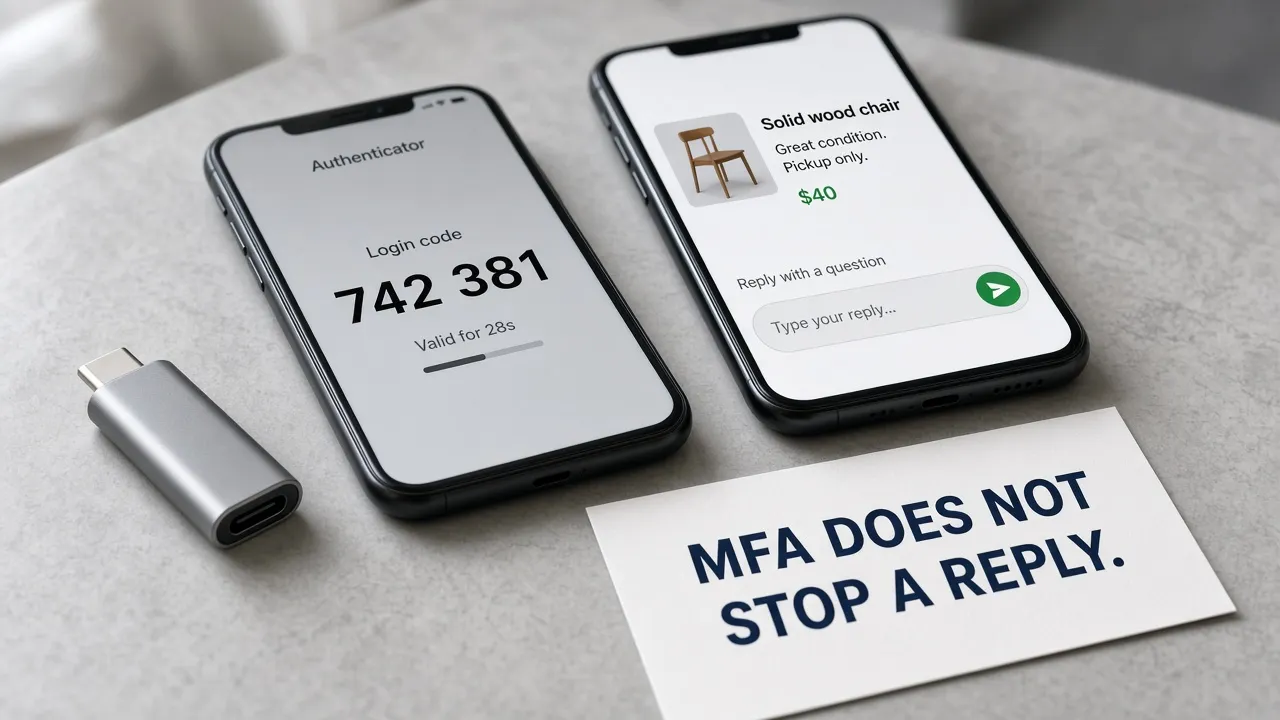
- Put a YubiKey (and an authenticator app) on the Facebook account so a later password theft is harder. MFA does not stop the first reply.
MFA: YubiKey and Google Authenticator
A hardware key or authenticator code does not stop a personalized text. It does protect the Facebook account if someone later tries the password. Grades match our MFA directory.
| Grade | Meaning |
|---|---|
| Fail | Documented second factor is SMS, voice, or email OTP |
| Pass | Self-serve Google Authenticator-style open TOTP |
| Strong | FIDO2 / YubiKey-class security key for sign-in |
| Platform | Grade | YubiKey | Authenticator |
|---|---|---|---|
| Strong | Yes | Yes | |
| Malwarebytes Account | Fail | No | No |
Facebook’s 2FA help names a security key, a third-party authenticator app, and SMS. Meta passkeys cover the account family. SMS still exists — enroll a key. Malwarebytes Account emails a code on every sign-in. That is email OTP, not Google Authenticator.
Directory: MFA support directory · Category → Social & Professional.
Recommended MFA tools
| Product | Best for | Get it |
|---|---|---|
| YubiKey 5C NFC | USB-C laptops + NFC phones | Amazon |
| YubiKey 5 NFC | USB-A desktops + NFC phones | Amazon |
| Proton Pass | Passkeys + authenticator-style TOTP | Proton Pass |
We may earn a commission if you buy a YubiKey or sign up for Proton Pass through the links above.
Independent cybersecurity audits
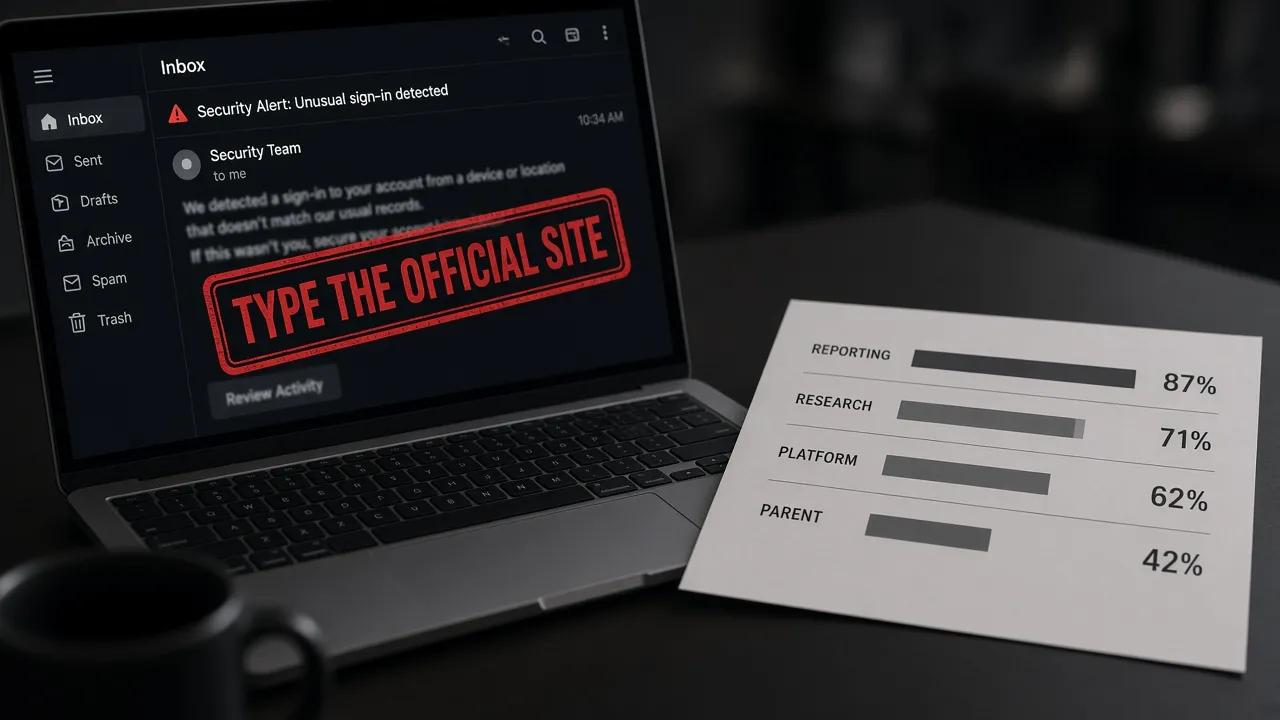
We audited reporting, researcher, and platform hosts on October 12, 2026. 100% is the ideal — none reach it. These scores are public email / transport / website posture. They do not mean Facebook was hacked.
| Organization | Domain | Overall | vs 100% |
|---|---|---|---|
| FBI IC3 | ic3.gov | 87% | −13 |
| Malwarebytes | malwarebytes.com | 71% | −29 |
| facebook.com | 62% | −38 | |
| Meta | meta.com | 42% | −58 |
| Domain | Identity | Transport | Website |
|---|---|---|---|
| ic3.gov | 90% | 45% | 97% |
| malwarebytes.com | 90% | 45% | 43% |
| facebook.com | 25% | 50% | 97% |
| meta.com | 25% | 15% | 37% |
Audit links: ic3.gov · malwarebytes.com · facebook.com · meta.com
facebook.com and meta.com Identity 25% means spoofed “Marketplace / security” mail is easier to deliver than the overall scores suggest. meta.com Transport 15% is the weak parent-company slice.
Website stack note
Passive website-tech probes on October 12, 2026:
| Domain | Stack signal |
|---|---|
| facebook.com | Undetected CMS; DigiCert TLS expires 2026-11-29 (47d) |
| meta.com | Undetected CMS; DigiCert TLS expires 2027-01-11 |
| malwarebytes.com | WordPress, version hidden; Amazon Trust TLS expires 2027-04-17 |
| ic3.gov | Undetected CMS; DigiCert TLS expires 2027-01-05 |
Point-in-time only. A marketing homepage is not a Marketplace-lure forensic finding.
Blacklist and lookalike domains
Email blacklist checks (public DoH, October 12, 2026): facebook.com, meta.com, malwarebytes.com, and ic3.gov were clear on mail/domain lists we can query.
DNS lookalike scans (BEC profile, registered signals only):
| Brand scanned | To review | Likely owned | BEC staging |
|---|---|---|---|
| facebook.com | 18 | 16 | 0 |
| meta.com | 30 | 1 | 0 |
| malwarebytes.com | 8 | 6 | 0 |
High-interest registered names (investigate; not proof this wave used them):
| Lookalike | Technique | Note |
|---|---|---|
| afacebook.com | insertion | Live NS + A + MX |
| facsebook.com | insertion | Live NS + A + MX |
| malwarebytes.app | tld-swap | Live NS + A + MX |
| malwarebytes.io | tld-swap | Live A + MX |
Many facebook.* TLD swaps CNAME back to Meta (likely owned), including .org, .co, and .us. Type facebook.com, not an extra-letter host. Continuous monitoring: Cybersquat Domain Monitoring.
Related coverage
- Chase card-hold SMS scam
- Houston brushing / unexpected-package QR
- FBI NCII / lookalike support phishing
- MFA support directory
Run a free audit at audit.emailmenow.com or contact EmailMeNow for DMARC / MTA-STS and phishing response aimed at the 100% ideal.
Sources: Malwarebytes — Marketplace name-and-number lure (Oct 6, 2026) · Meta — Marketplace safety · Facebook 2FA · Meta passkeys · facebook.com/hacked · Malwarebytes Account email verification · IC3. Independent EmailMeNow audits, website-tech, blacklist, cybersquat, and CourtListener searches October 12, 2026. Domain scores: audit.emailmenow.com only.