Click2Houston warned Houston viewers on September 15, 2026: an unexpected package can be a brushing scam, and the real hit is often the QR code, link, or “return” note inside — not the cheap lotion or hair product. Scan that code and you can land on a phishing site or install malware.
This is not a report that Amazon, Temu, USPS, or the FTC were hacked. It is a consumer-alert phishing pattern. The FTC published the same QR-inside-the-box warning on August 20, 2026. The FBI IC3 flagged the QR variation on July 31, 2025.
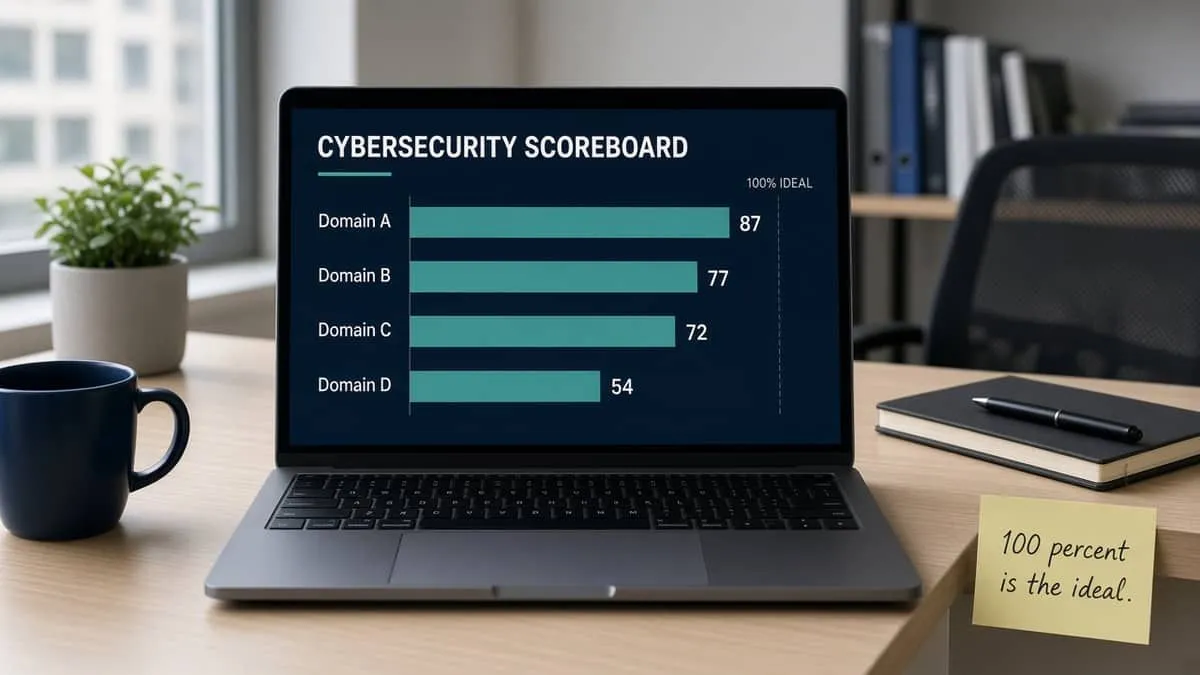
We scanned ic3.gov, usps.com, ftc.gov, and amazon.com. 100% is the ideal overall domain-security score. None reach it.
Snapshot
| Field | Detail |
|---|---|
| Local alert | Click2Houston · Sept 15, 2026 |
| Federal alert | FTC · Aug 20, 2026 |
| QR / malware PSA | FBI IC3 I-073125-PSA · July 31, 2025 |
| Postal guidance | USPIS — Brushing Scam |
| Report | ReportFraud.ftc.gov · ic3.gov |
Two scams in one box
Classic brushing is a fake-review trick. A seller ships something you never ordered — often under a known marketplace name — then uses the delivery as “proof” you bought it so they can post a review in your name. The FTC says recent reports describe cheap, random items: baby wipes, toothpaste, seeds.
The phishing twist is what Houston TV is stressing. The Postal Inspection Service calls it quishing: a card that says scan to learn who sent the gift or how to return it. The FBI says packages often arrive without a sender so you feel you have to scan. The site can harvest card numbers, usernames, and passwords, or drop malware that steals data from the phone.
Click2Houston cites the Better Business Bureau on the same don’t-scan, don’t-click advice. Treat a lookalike Amazon or eBay label as a costume, not proof the real retailer sent it.
What to do with the package
Federal and local advice overlap on the dangerous part: do not scan the QR code, click the link, or follow the card’s return website.
| Step | Why |
|---|---|
| Leave the code unscanned | QR can open a phishing page or malware |
| Change shopping passwords | Address on the box may mean the account was already abused |
| Message the real retailer | FTC: tell Amazon or the marketplace so they can pull a fake seller |
| Check credit | AnnualCreditReport.com weekly |
Keeping it. The FTC says you generally may keep unordered merchandise and are not required to pay or return it. USPIS says the same if you opened it and want it — and that you may throw it away if it is safe. USPIS also says an unopened box with a return address can be marked RETURN TO SENDER. Click2Houston’s local warning is stricter: don’t try to return using the package’s own instructions. Those two are compatible if you treat the card’s QR / “return portal” as the trap, not a USPS window.
Do not eat, plant, or use mystery seeds, food, or unknown liquids. USPIS: call the proper authorities for organic or unknown contents.
If you already scanned and typed a password, change that password now, turn on a stronger second factor, and report the lure.
MFA on the accounts this lure hunts
A QR page that looks like Amazon or USPS still works if you type the password. Hardware keys and authenticator apps raise the cost after you lock the real account. They do not make a porch QR safe.
| Grade | Meaning |
|---|---|
| Fail | SMS, email OTP, or no public key / open TOTP |
| Pass | Self-serve Google Authenticator-style open TOTP |
| Strong | FIDO2 / YubiKey-class security key for sign-in |
| Platform | Grade | YubiKey | Authenticator |
|---|---|---|---|
| Amazon shopping | Fail | No | Yes |
| USPS / Informed Delivery | Fail | No | Yes |
Amazon’s two-step help documents a code by text message or authenticator app. Passkeys exist on the shopping account. Amazon does not name a YubiKey enrollment button for retail two-step. SMS stays in the public docs, so the row stays Fail. (AWS IAM security keys are a different login.)
USPS MFA help and the August 17, 2026 customer guide name SMS, email OTP, or an authenticator app — including Google Authenticator. New accounts after March 6, 2025 must enroll; older accounts can skip. USPS does not name YubiKey. SMS and email OTP keep the row Fail. Enroll the authenticator anyway, and use Informed Delivery to see what is actually coming — do not treat a digest email link as automatically safe.
Directory: MFA support directory · Category → Business Apps.
Recommended MFA tools
| Product | Best for | Get it |
|---|---|---|
| YubiKey 5C NFC | USB-C laptops + NFC phones | Amazon |
| YubiKey 5 NFC | USB-A desktops + NFC phones | Amazon |
| Proton Pass | Passkeys + authenticator-style TOTP | Proton Pass |
We may earn a commission if you buy a YubiKey or sign up for Proton Pass through the links above.
Independent cybersecurity audits
We audited the official report, postal, regulator, and marketplace hosts on September 20, 2026. 100% is the ideal — none reach it. These scores are public email / transport / website posture. They do not mean a retailer was breached.
| Organization | Domain | Overall | vs 100% |
|---|---|---|---|
| FBI IC3 | ic3.gov | 87% | −13 |
| USPS | usps.com | 77% | −23 |
| Federal Trade Commission | ftc.gov | 72% | −28 |
| Amazon | amazon.com | 54% | −46 |
| Domain | Identity | Transport | Website |
|---|---|---|---|
| ic3.gov | 90% | 45% | 97% |
| usps.com | 75% | 15% | 87% |
| ftc.gov | 95% | 45% | 40% |
| amazon.com | 55% | 15% | 37% |
Audit links: ic3.gov · usps.com · ftc.gov · amazon.com
usps.com and amazon.com sit at 15% transport (MTA-STS / related). A spoofed “your package / return this item” message is easier to deliver than the overall scores suggest. Type usps.com and amazon.com yourself. Do not use the QR.
Postal Inspection Service host uspis.gov scored 53% (Identity 50 / Transport 45 / Website 37). Use it as the guidance page, not a login you reach from a box card.
Website stack
Passive homepage + Certificate Transparency probes (September 20, 2026). Versions only — not a claim the sites were compromised.
| Domain | Stack note |
|---|---|
| ic3.gov | CMS undetected; DigiCert TLS expires 2027-01-05 |
| usps.com | CMS undetected; Sectigo TLS expires 2027-03-25 |
| ftc.gov | Drupal 10 (probe latest 11.4.7); IdenTrust TLS expires 2027-03-01 |
| amazon.com | CMS undetected; DigiCert TLS expires 2027-01-23 |
| uspis.gov | CMS undetected; Sectigo TLS expires 2027-03-25; HTTP→HTTPS redirect not confirmed on probed hosts |
Drupal 10 vs 11.x on ftc.gov is a probe comparison, not a brushing finding.
Blacklist and lookalikes
Email blacklist checks (public DoH, September 20, 2026): ic3.gov, ftc.gov, and amazon.com were clear on mail/domain lists we can query. usps.com and uspis.gov share Proofpoint-hosted MX; one IP showed SpamRATS all. That is shared-gateway noise, not a finding that USPS is a spam source. We do not lead on it.
Registered lookalikes that matter for this lure (BEC / standard squat scan):
| Lookalike | Technique | Signal |
|---|---|---|
| amaz0n.com / ama2on.com | homoglyph | Live NS + A |
| aazon.com | omission | NS + A + MX |
| amazon.net | TLD swap | NS + A + MX |
| iusps.com / usp5.com | insert / homoglyph | NS + A + MX |
| usps.org | TLD swap | NS + A + MX |
| ic3.com | TLD swap | BEC staging (NS + MX, no site A) |
| ftc.biz | TLD swap | BEC staging (NS + MX) |
Amazon also owns many defensive redirects (amazon.org, aamazon.com, and peers). Type amazon.com, usps.com, ftc.gov, and ic3.gov — not a near-spell from a package card. Continuous monitoring: Cybersquat Domain Monitoring.
CourtListener RECAP searches for “brushing scam,” quishing, and unsolicited package + QR did not turn up a matching 2025–2026 federal QR-package docket. This remains a consumer-alert story, not a filed Houston case we can cite.
Related coverage
- BBB / FTC “You’re Invited” party-invite phishing
- Montrose tap-to-pay wallet fraud
- Shopify Shop fake-invoice scam
- PA AG MyChart phishing
- MFA support directory
Sources: Click2Houston, Sept 15, 2026 · FTC — unexpected package / brushing, Aug 20, 2026 · FBI IC3 PSA I-073125-PSA · USPIS — Brushing Scam · Amazon two-step verification and passkeys · USPS MFA FAQ. Independent EmailMeNow audits, website-tech, blacklist, cybersquat, and CourtListener searches September 20, 2026. Domain scores: audit.emailmenow.com only.