McKesson Corporation — the Irving, Texas drug distributor and healthcare-technology company traded as MCK — confirmed a cybersecurity incident that targeted employee corporate accounts between August 20 and August 25, 2026. Its September 8 notice says data was taken from third-party applications, and that personal and protected health information may be in the set.
This is not a duplicate of the Nutex Health Item 1.05. That August Nutex recap only pointed at McKesson’s earlier service-degradation coverage as a sibling. It is also not the MSG / ShinyHunters vishing or CNO Services vishing stories — different victims.
The new hook in this week’s Texas phishing/ransomware alert pile is the lawsuit wave. Law.com (September 11) reported at least a dozen class actions in northern Texas, including Hall v. McKesson Corp. and CoverMyMeds LLC. CourtListener now shows 15 N.D. Tex. dockets from August 30 through September 10, 2026.
McKesson has not named a crew and has not called the incident material in its 8-K. Treat ShinyHunters, the 284 million records figure, and the voice-phishing of two employees as claims unless McKesson confirms them.
Snapshot
| Field | Detail |
|---|---|
| Company | McKesson Corp. (NYSE: MCK) · HQ Irving, TX |
| Window | Aug 20–25, 2026 (company notice) |
| SEC filing | Item 7.01 8-K dated Aug 28 — not Item 1.05 |
| Actor | ShinyHunters claimed; not named by McKesson |
| CourtListener | 15 N.D. Tex. suits · first Hall 3:26-cv-02958 · Aug 31 |
What McKesson has confirmed
The August 28 Item 7.01 Form 8-K said McKesson discovered a cybersecurity incident on August 25 and pointed readers to mckesson.com/cybersecurity. As of that filing it had not determined the incident was material or likely to hit results. That is FD disclosure, not the material-incident box Nutex used.
The September 8 substitute notice is more specific:
- Employee corporate accounts were targeted.
- The window is August 20–25.
- McKesson is a vendor to providers, so PHI may be in the copied set.
- Possible data includes names, addresses, emails, patient IDs, dates of birth, insurance IDs, diagnoses and medicines, billing / card / bank fields, and Social Security numbers — not the same for every person.
- Patients, guarantors, and others may be in scope. Individual notices come later, through customers.
- A call center is at 1-855-760-5202. HQ in the notice: 6555 State Highway 161, Irving, TX 75039.
Do not treat a missing Texas OAG row yet as “no Texans were affected.” The company says the review is early.
What ShinyHunters claimed — and what the lawsuits say
HIPAA Journal and CyberScoop reported that ShinyHunters listed McKesson and claimed about 1 TB taken from Salesforce / Snowflake, a ransom above $55 million, and 284 million raw records (rows, not unique patients). CyberInsider said the group told them they voice-phished two employees. McKesson declined to confirm the actor or those counts.
Law.com’s September 11 piece is the lawsuit story: at least a dozen northern Texas complaints accuse McKesson of failing to protect patient data and of slow disclosure. The article names Hall v. McKesson Corp. and CoverMyMeds LLC.
CourtListener RECAP (checked September 12, 2026) lists 15 N.D. Texas dockets captioned against McKesson Corporation, filed August 30–September 10. Examples:
These are alleged class actions. They do not prove the vishing path in court. They do show how fast a vendor PHI incident becomes Texas federal litigation.
What patients and clinics should do
- Type mckesson.com or the official notice yourself. Do not use a “McKesson settlement / IDX / credit-monitor” link from email or text.
- If you paid a bill or received care through a McKesson oncology, multispecialty, medical-surgical, or CoverMyMeds workflow, watch EOBs and credit. Enroll in the company’s IDX offer only from a host you typed.
- Clinics: assume follow-on fake IT callbacks and fake prior-auth portals. Call back a number already on file.
- Freeze credit and report misuse at IdentityTheft.gov and IC3.
- A hardware key does not un-copy files that already left. It does cut a lot of the callback and fake-login wave that follows this headline.
MFA: YubiKey and Google Authenticator
Voice phishing beats SMS and many push prompts: the caller asks you to read a code or approve a prompt. Grades match our MFA directory.
| Grade | Meaning |
|---|---|
| Fail | Documented second factor is SMS, voice, or email OTP — or no public path |
| Pass | Self-serve Google Authenticator-style open TOTP |
| Strong | FIDO2 / YubiKey-class security key for sign-in |
| Platform | Grade | YubiKey | Authenticator |
|---|---|---|---|
| McKesson | Fail | No | No |
| CoverMyMeds | Fail | No | No |
Public McKesson 2FA help for US Oncology / Ontada points staff to the proprietary McKesson Authenticator app (push + in-app TOTP) via selfservice.usoncology.com. That is a vendor-locked token. There is no public retail YubiKey or Google Authenticator enrollment path. CoverMyMeds patient/provider pages we checked do not name either method. A locked app does not stop a voice callback.
Directory: MFA support directory · Category → Healthcare.
Recommended MFA tools
| Product | Best for | Get it |
|---|---|---|
| YubiKey 5C NFC | USB-C laptops + NFC phones | Amazon |
| YubiKey 5 NFC | USB-A desktops + NFC phones | Amazon |
| Proton Pass | Passkeys + authenticator-style TOTP | Proton Pass |
We may earn a commission if you buy a YubiKey or sign up for Proton Pass through the links above.
Independent cybersecurity audits
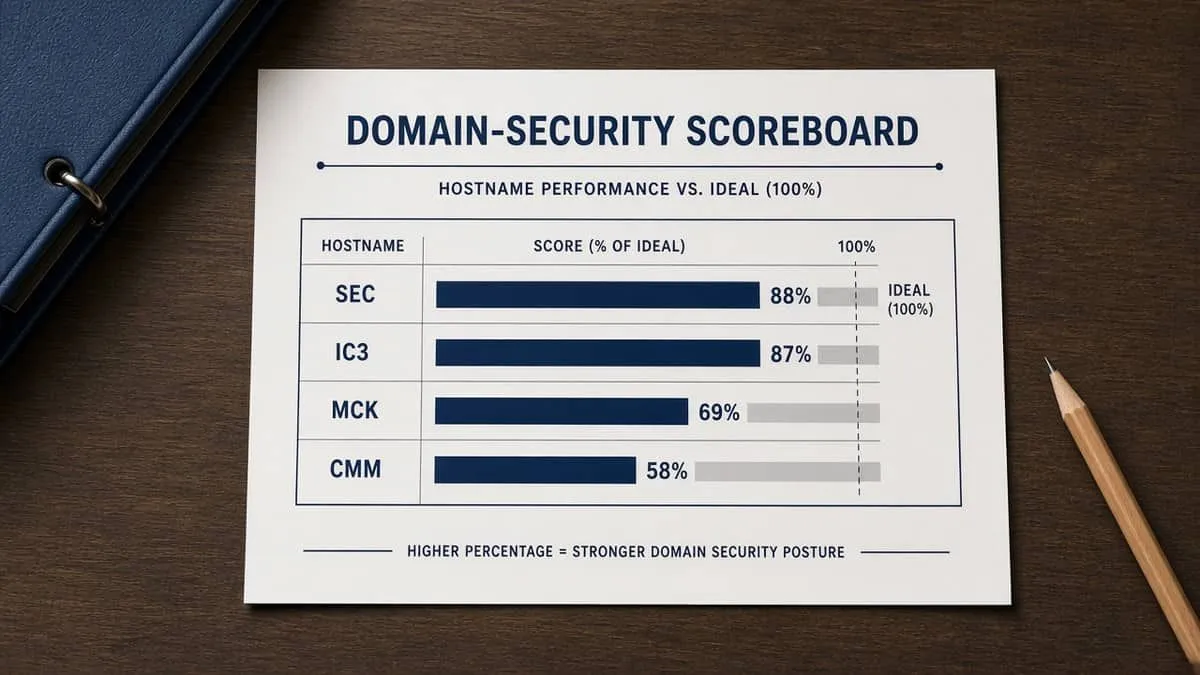
We audited the official McKesson, CoverMyMeds, SEC, and reporting hosts on September 12, 2026. 100% is the ideal — none reach it. These scores are public email / transport / website posture. They do not prove how the accounts were phished.
| Organization | Domain | Overall | vs 100% |
|---|---|---|---|
| U.S. SEC | sec.gov | 88% | −12 |
| FBI IC3 | ic3.gov | 87% | −13 |
| McKesson | mckesson.com | 69% | −31 |
| CoverMyMeds | covermymeds.com | 58% | −42 |
| Domain | Identity | Transport | Website |
|---|---|---|---|
| sec.gov | 90% | 45% | 98% |
| ic3.gov | 90% | 45% | 97% |
| mckesson.com | 90% | 15% | 42% |
| covermymeds.com | 65% | 15% | 37% |
Audit links: sec.gov · ic3.gov · mckesson.com · covermymeds.com
mckesson.com at 69% is still −31 from the ideal. Transport 15% on both McKesson hosts is a mail-transport gap — not a reason to trust a “McKesson IT” callback. sec.gov is the 8-K host. ic3.gov is the reporting host.
Website stack note
Passive website-tech probes on September 12, 2026:
| Domain | Stack signal |
|---|---|
| mckesson.com | Stack undetected; DigiCert TLS expires 2027-03-15 |
| covermymeds.com | Stack undetected; DigiCert TLS expires 2027-03-26 |
| sec.gov | Drupal (version hidden); DigiCert TLS expires 2027-03-02 |
| ic3.gov | Stack undetected; DigiCert TLS expires 2027-01-05 |
Point-in-time only. A live marketing homepage is not a forensic finding on the vishing path.
Blacklist and lookalike domains
Email blacklist checks (public DoH, September 12, 2026): mckesson.com, sec.gov, and ic3.gov were clear on mail/domain lists we can query. covermymeds.com showed an informational SPFBL hit on a shared Proofpoint MX — not a reason to lead “CoverMyMeds is blacklisted.” SEC web/CDN IPs also showed SPFBL notes. Do not lead as “McKesson is blacklisted.”
DNS lookalike scans (BEC profile, registered signals only):
| Brand scanned | To review | Likely owned | BEC staging |
|---|---|---|---|
| mckesson.com | 37 | 2 | 4 |
| covermymeds.com | 22 | 0 | 0 |
| sec.gov | 14 | 0 | 0 |
| ic3.gov | 15 | 0 | 1 |
High-interest registered names (investigate; not proof this incident used them):
| Lookalike | Technique | Note |
|---|---|---|
| mckeason.com | adjacent-key | BEC staging (NS + MX) |
| mckess0n.com | homoglyph | BEC staging (NS + MX) |
| mckessoin.com | insertion | BEC staging (NS + MX) |
| mckessons.com | insertion | BEC staging (NS + MX) |
| ic3.com | tld-swap | BEC staging — not the .gov bureau |
| sec.com | tld-swap | Live .com — not the Commission |
mckesson.net and mckesson.org point at the brand. Type mckesson.com, not a one-letter swap. Continuous monitoring: Cybersquat Domain Monitoring.
Related coverage
- Nutex Health data breach — The Gentlemen claimed
- CNO Services vishing — Texas OAG
- MSG Sports ShinyHunters vishing
- Houston City College / ShinyHunters
- MFA support directory
Run a free audit at audit.emailmenow.com or contact EmailMeNow for DMARC / MTA-STS and phishing-resistant MFA aimed at the 100% ideal.
Sources: McKesson notice of data breach (Sept 8, 2026) · McKesson Item 7.01 8-K (filed Aug 28) · Law.com (Sept 11) · HIPAA Journal · CyberScoop · CyberInsider · CourtListener N.D. Tex. RECAP searches September 12, 2026 (Hall 3:26-cv-02958). Independent EmailMeNow audits, website-tech, blacklist, and cybersquat September 12, 2026. Domain scores: audit.emailmenow.com only. Google Alerts weekly scan used as a lead, not as confirmation.