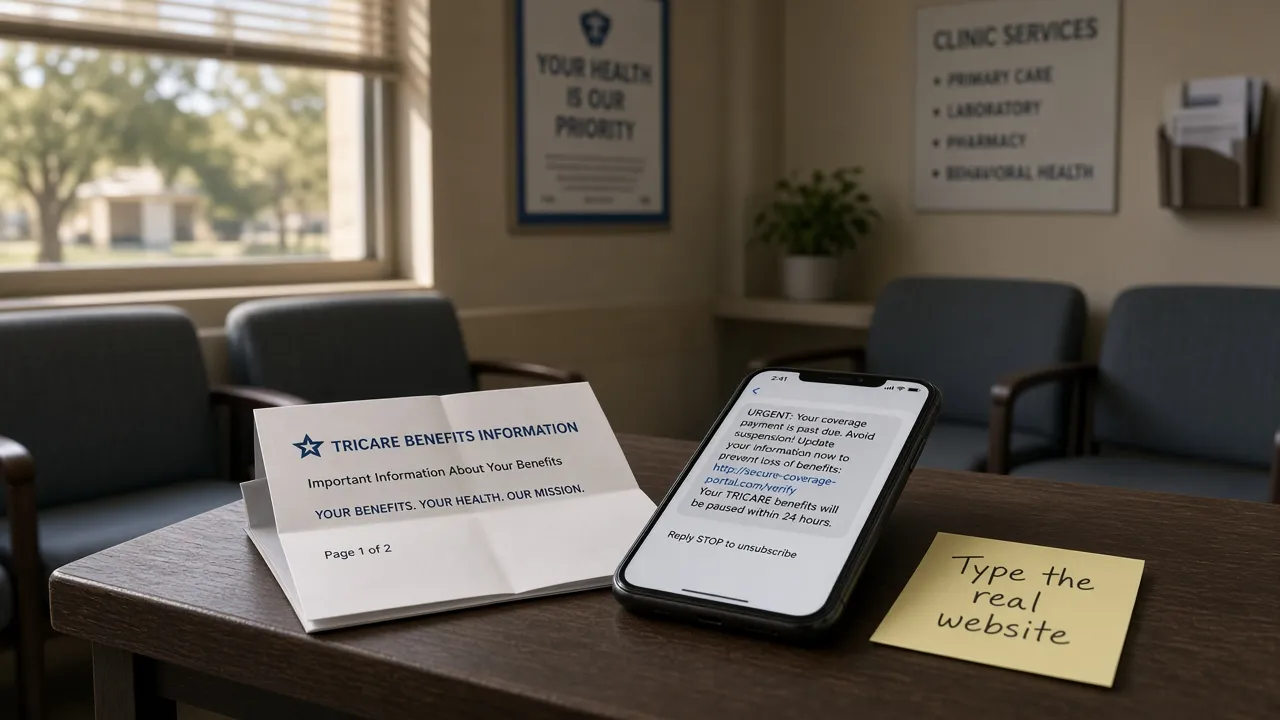
Joint Base San Antonio republished a Defense Health Agency warning: if a call, text, email, or letter claims to be TRICARE and asks you to pay, “confirm” coverage, or hand over a Social Security number, DoD ID, bank details, or health information, it is a scam. The same copy sits on the TRICARE Newsroom. Fort Sam Houston is the local Texas hook. Military OneSource’s phishing primer is the cited background.
This is an official PSA, not a reported breach of TRICARE, JBSA, Humana Military, or TriWest. Kathy McGuire, chief of the TRICARE Health Plan managed-care support branch at DHA, said scammers “may try to target anyone with TRICARE coverage.”
Official pages: JBSA — Don’t be a target of scams about TRICARE · TRICARE Newsroom
Snapshot
| Field | Detail |
|---|---|
| Alert | TRICARE / DHA phishing PSA · JBSA reprint |
| Texas hook | Fort Sam Houston / Joint Base San Antonio |
| Platform breach | Not reported |
| CourtListener | 0 matching Oct 2026 TRICARE-phishing dockets |
| Report | Your regional contractor or DHA Inspector General |
TRICARE and its contractors will not call or text to collect payment or offer discounts. They will not ask for SSN, DoD ID, banking, or health data that way. tricare.mil/fraud repeats the same rule and notes a separate Berkeley Research Group / Express Scripts privacy incident — that vendor notice is not this PSA.
How the lure lands
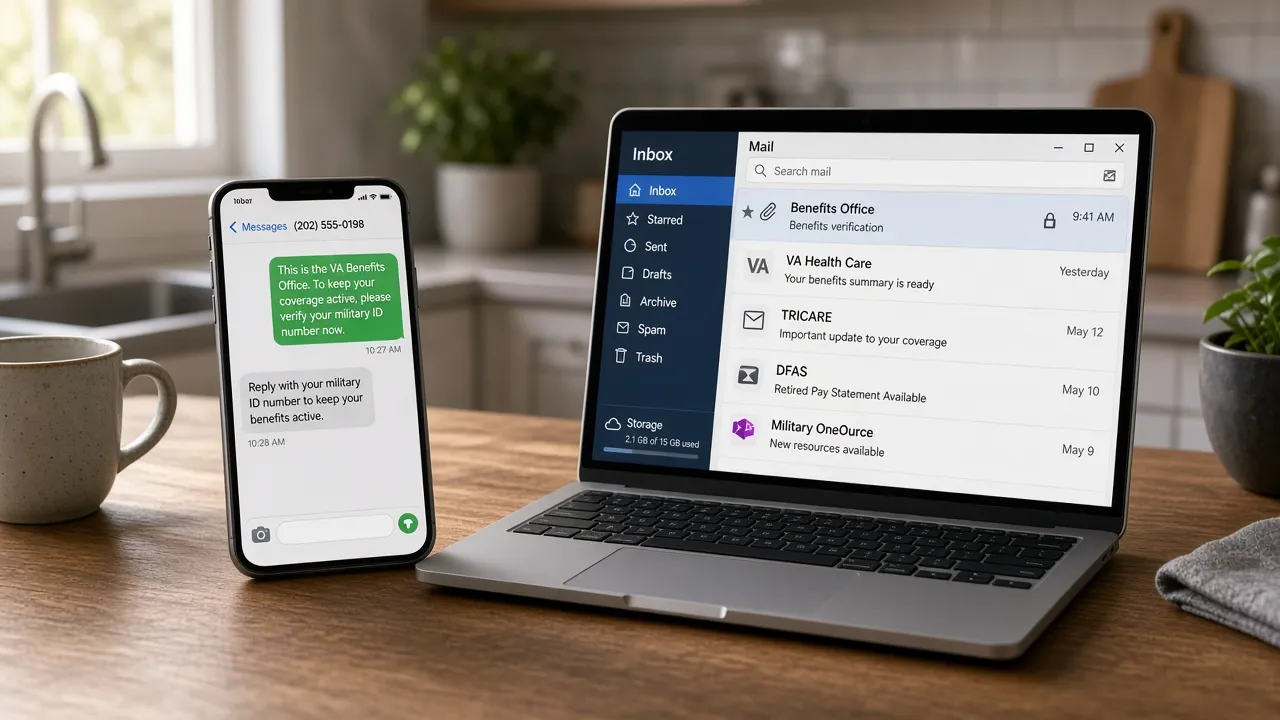
JBSA and the Newsroom describe the usual military-community mix: a voicemail about a “suspended” ID card, a text about a leftover TRICARE bill, an email with a “secure” portal that is not tricare.mil. Military OneSource groups those as phishing aimed at people who already expect official mail.
The same week, TRICARE is moving logins from legacy DS Logon to myAuth. milConnect and ID Card Office Online have already switched. East (Humana Military), West (TriWest), Overseas (International SOS), TRICARE For Life (WPS), pharmacy (Express Scripts), dental (United Concordia), and MHS GENESIS are still transitioning through FY26, per the May 5, 2026 Newsroom explainer and the myAuth page (updated October 6, 2026). A “your DS Logon expires tonight — click here” message is exactly the kind of mail this PSA is about.
What beneficiaries should do
- Type tricare.mil or tricare.mil/dslogon. Do not use a link from unexpected mail or a text.
- If someone asks for payment, SSN, DoD ID, or a one-time code, hang up. Call the number you already have for your contractor.
- Keep your address and email current in milConnect so real mail does not bounce to a stranger.
- Report the contact to your contractor (Humana Military in the East, TriWest in the West) or the DHA Office of Inspector General. You can stay anonymous.
- If you already typed a password on a fake page, change it on the real host and tell the contractor.
MFA: YubiKey and Google Authenticator
A hardware key does not stop a voice callback. It does stop a lot of the “reset your myAuth / DS Logon” pages that harvest passwords and SMS codes. Grades match our MFA directory.
| Grade | Meaning |
|---|---|
| Fail | SMS, voice, or email OTP — or no public path |
| Pass | Self-serve Google Authenticator-style open TOTP |
| Strong | FIDO2 / YubiKey-class security key for sign-in |
| Platform | Grade | YubiKey | Authenticator |
|---|---|---|---|
| Login.gov | Strong | Yes | Yes |
| TRICARE / myAuth | Fail | No | No |
Login.gov is the civilian federal comparison: a security key plus apps including Google Authenticator. TRICARE’s public myAuth pages name a CAC, username/password plus “a secure multi-factor authentication method,” and Okta Verify. They do not name a self-serve YubiKey or Google Authenticator. Okta Verify is a vendor-locked app, not open TOTP. A DoD CIO MFA memo still allows SMS OTP on myAuth when SMS is allowed. That keeps the beneficiary story at Fail. A CAC is strong for people who have one. It is not a YubiKey enrollment path we can grade for families and retirees.
Directory: MFA support directory · Category → Healthcare.
Recommended MFA tools
| Product | Best for | Get it |
|---|---|---|
| YubiKey 5C NFC | USB-C laptops + NFC phones | Amazon |
| YubiKey 5 NFC | USB-A desktops + NFC phones | Amazon |
| Proton Pass | Passkeys + authenticator-style TOTP | Proton Pass |
We may earn a commission if you buy a YubiKey or sign up for Proton Pass through the links above.
Independent cybersecurity audits
We audited TRICARE, JBSA, Military OneSource, and the East-region contractor on October 11, 2026. 100% is the ideal — none reach it. These scores are public email / transport / website posture. They do not prove a TRICARE breach.
| Organization | Domain | Overall | vs 100% |
|---|---|---|---|
| Military OneSource | militaryonesource.mil | 85% | −15 |
| Humana Military | humanamilitary.com | 78% | −22 |
| MHS / DHA | health.mil | 71% | −29 |
| TRICARE | tricare.mil | 68% | −32 |
| JBSA | jbsa.mil | 59% | −41 |
| TriWest | triwest.com | 62% | −38 |
| Domain | Identity | Transport | Website |
|---|---|---|---|
| militaryonesource.mil | 95% | 45% | 84% |
| humanamilitary.com | 75% | 15% | 90% |
| health.mil | 95% | 45% | 37% |
| tricare.mil | 95% | 45% | 37% |
| triwest.com | 75% | 15% | 37% |
| jbsa.mil | 70% | 45% | 40% |
Audit links: tricare.mil · jbsa.mil · health.mil · militaryonesource.mil · humanamilitary.com · triwest.com
TRICARE Identity 95% is the bright spot. Transport 45% (and Humana / TriWest 15%) means a fake “Humana Military / update myAuth” message can still land without MTA-STS enforce. tricare.mil and jbsa.mil showed no MX in this probe — web posture only. jbsa.mil overall 59% is the Fort Sam reprint host, not a clinic-records finding.
Website stack note
Passive website-tech probes on October 11, 2026:
| Domain | Stack signal |
|---|---|
| tricare.mil | ASP.NET; DigiCert TLS expires 2026-12-18; HTTP→HTTPS not confirmed |
| health.mil | ASP.NET; same DigiCert expiry 2026-12-18 |
| jbsa.mil | Stack undetected; HTTP→HTTPS not confirmed |
| militaryonesource.mil | WordPress (reported 1.13.8 vs current core); IdenTrust TLS expires 2027-03-21 |
| humanamilitary.com | Stack undetected; DigiCert TLS expires 2027-02-09 |
| triwest.com | ASP.NET; GoDaddy TLS expires 2027-04-11 |
Point-in-time only. A public homepage stack is not a finding on a beneficiary mailbox.
Blacklist and lookalike domains
Email blacklist checks (public DoH, October 11, 2026): tricare.mil, health.mil, militaryonesource.mil, humanamilitary.com, and triwest.com were clear on mail/domain lists we can query. jbsa.mil returned no IPs in this probe. SPFBL notes on TRICARE and Military OneSource web/CDN addresses are informational — not mail-reputation hits.
DNS lookalike scans (BEC profile, registered signals only):
| Brand scanned | To review | Likely owned | BEC staging |
|---|---|---|---|
| tricare.mil | 6 | 0 | 0 |
| jbsa.mil | 4 | 0 | 0 |
| humanamilitary.com | 1 | 0 | 0 |
High-interest registered names (investigate; not proof this PSA named them):
| Lookalike | Technique | Note |
|---|---|---|
| tricare.com / .org / .net | tld-swap | Not the .mil program |
| jbsa.com / .org / .us | tld-swap | Live DNS |
| humanamilitary.org | tld-swap | Live NS + A + MX |
Type tricare.mil and jbsa.mil. Continuous monitoring: Cybersquat Domain Monitoring.
Related coverage
- HHSC STEPS / PFD phishing
- Texas Cyber Command / Cyber Ready
- FBI NCII lookalike support phishing
- PA AG MyChart phishing
- MFA support directory
Run a free audit at audit.emailmenow.com or contact EmailMeNow for DMARC / MTA-STS and phishing response aimed at the 100% ideal.