Retail “Wi-Fi jammer” gadgets marketed to burglars are usually 802.11 deauthentication tools, not broadband RF jammers. A deauth attacker forges management disconnect frames; on WPA2 networks without Protected Management Frames (802.11w) enforced, those frames can knock cameras and doorbells offline while the rest of the LAN keeps working. WPA3-Personal makes PMF mandatory, which blocks classic deauth attacks against the Wi-Fi link. A true RF jammer still disrupts any wireless camera on any WPA version — no consumer Wi-Fi setting fixes that.
We used us.eufy.com product specs, device FAQs on service.eufy.com, and the Dec 2022 community disclosure for cameras and doorbells only. Last checked: October 20, 2026. When Eufy does not publish a field, we label it Not published.
Series: 11-brand WPA3 / 5 GHz / PMF hub · Wyze baseline
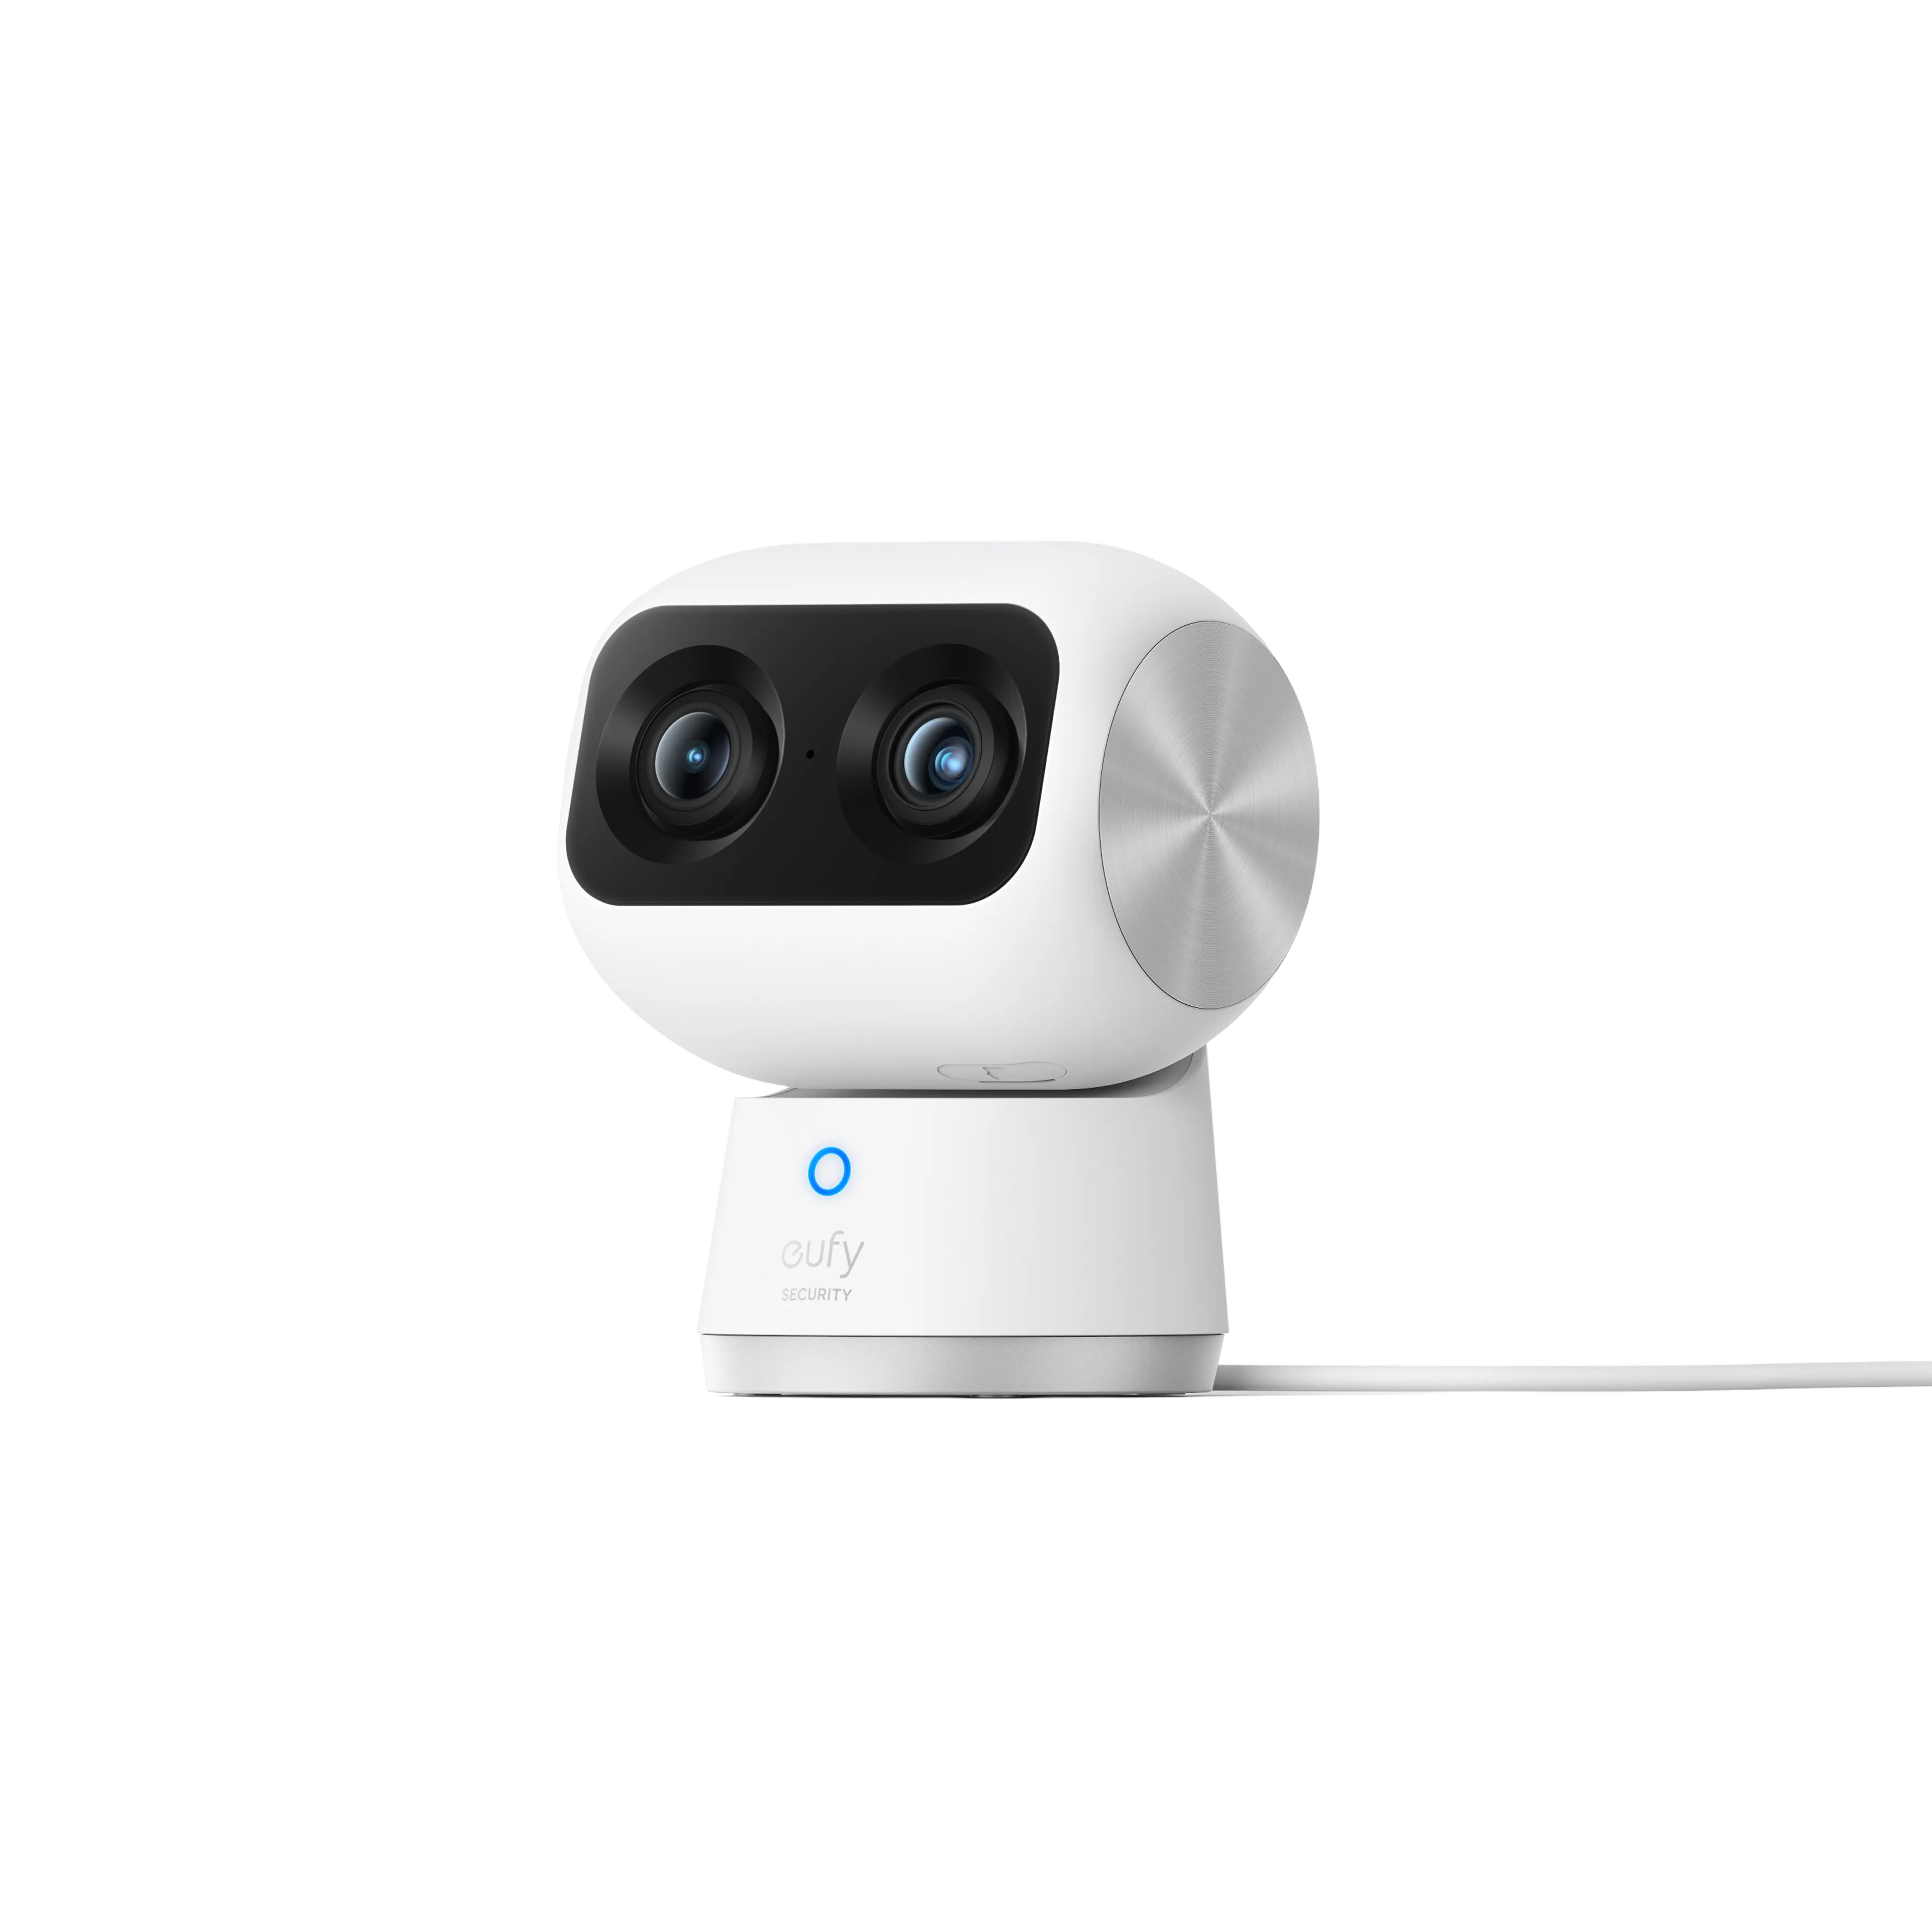
Product image: Eufy Indoor Cam S350 — courtesy of Eufy.
Snapshot
| Field | Detail |
|---|---|
| WPA3 | Video Doorbell S4 lists WPA/WPA2/WPA3; Indoor Cam S350 and Floodlight E340 document WPA3 in FAQs |
| 5 GHz | S350, E340, Doorbell S4 — 2.4 + 5 GHz; eufyCam S4 / S3 Pro and Wall Light Cam S4 are 2.4 GHz only |
| PMF | Not published |
| Audit | eufy.com 57% |
Doorbells and dual-band plug-in / floodlight
| Product | Bands (Eufy docs) | WPA (Eufy docs) | PMF |
|---|---|---|---|
| Video Doorbell S4 | 2.4 + 5 GHz; 802.11 b/g/n/ac/ax | WPA / WPA2 / WPA3 | Not published |
| Floodlight Cam E340 | 2.4 + 5 GHz; Wi-Fi 6 | WPA3 (FAQ) | Not published |
| Indoor Cam S350 | 2.4 + 5 GHz; 802.11ax | WPA3 (FAQ) | Not published |
Sources: Doorbell S4 · E340 · S350
Battery and 2.4 GHz-only SKUs
| Product | Bands | WPA | PMF |
|---|---|---|---|
| eufyCam S4 | 2.4 GHz; 802.11 b/g/n/ax | Not published | Not published |
| eufyCam S3 Pro | 2.4 GHz; 802.11 b/g/n | Not published | Not published |
| Wall Light Cam S4 | 2.4 GHz only | Not published | Not published |
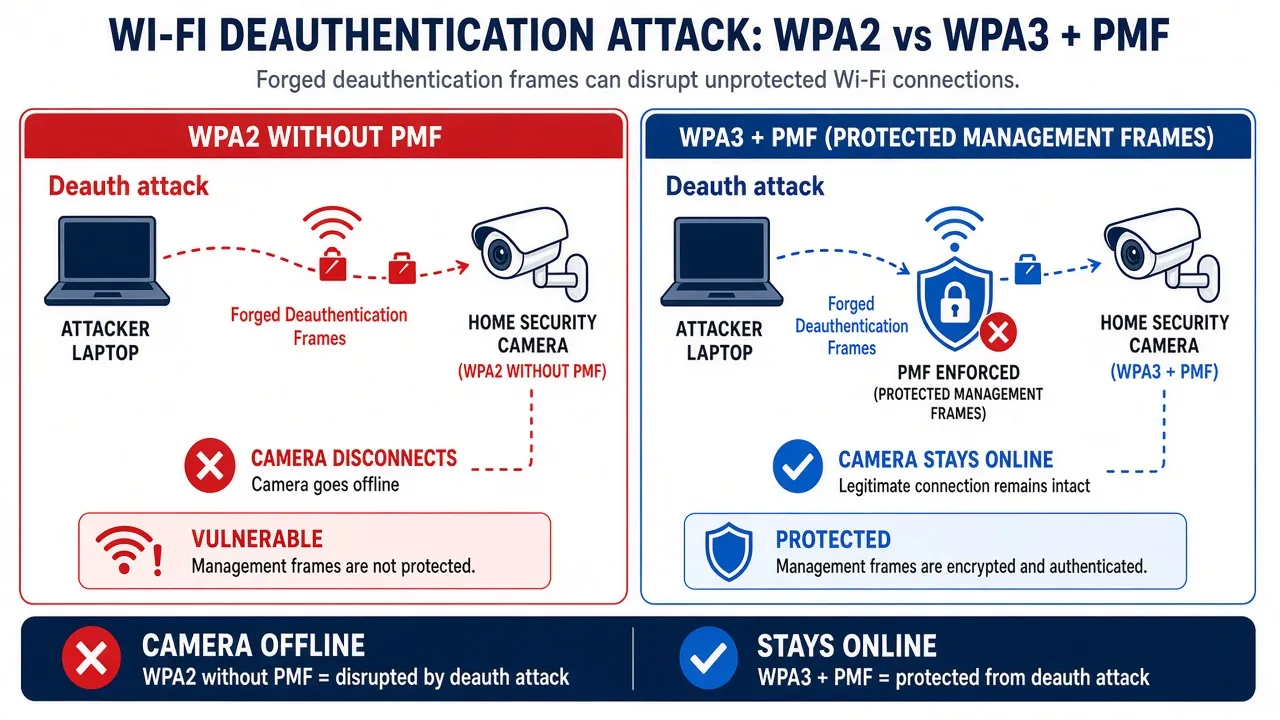
Illustration: deauth vs WPA3/PMF — not a vendor diagram.
Wi-Fi security risks: WEP through WPA3
The product tables in this post describe what each vendor publishes about its gear. Separately, every owner should understand how legacy Wi-Fi security modes fail in the real world. Attacks differ: some require capturing traffic and offline guessing; others require only radio range and affect availability — not decryption.
WEP and WPA (TKIP)
WEP (Wired Equivalent Privacy) was broken years ago: passive capture plus commodity tools can recover a WEP key in minutes on busy networks. The Wi-Fi Alliance and industry guidance treat WEP as obsolete — do not operate IoT or cameras on WEP. WPA with TKIP replaced WEP but is also deprecated; modern certification programs expect AES (CCMP) and WPA2 or WPA3.
WPA2-Personal (PSK)
WPA2-PSK is still common on routers and IoT SSIDs. Its weaknesses are well documented:
- Offline passphrase attacks. An attacker who records a valid 4-way handshake or a router PMKID (where the AP exposes it) can attempt offline dictionary attacks against the passphrase. Short or reused passwords fall quickly; a long, random passphrase makes offline guessing impractical in practice. This is realistic on WPA2-PSK when the password is weak — not when the passphrase is strong.
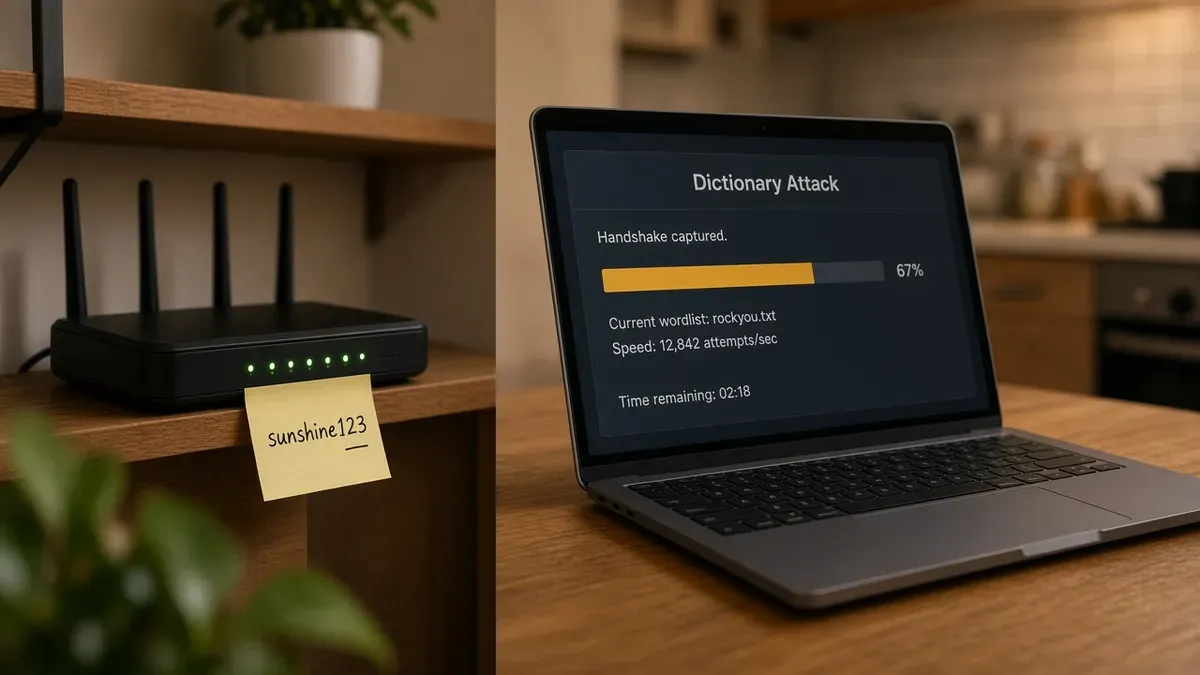
Illustration: a captured handshake plus a guessable passphrase — not a substitute for router sticker photos in real incidents. - Neighbors or guests on your PSK. Anyone with the Wi-Fi password can join the LAN like a trusted device. That often means their traffic exits through your public IP address, which can complicate abuse complaints or law-enforcement inquiries. Segment IoT and rotate the passphrase if you suspect sharing — see NIST WLAN guidance below.
Shared passwords are convenient; they also mean your IP can carry someone else’s activity. - On-LAN reach to your devices. Joining the Wi-Fi does not automatically grant control of every camera, oven, or laptop. It does place an attacker on the same broadcast domain, where they can probe for unpatched firmware, default credentials, and unencrypted local traffic. VLANs, guest networks, and device updates reduce that exposure.
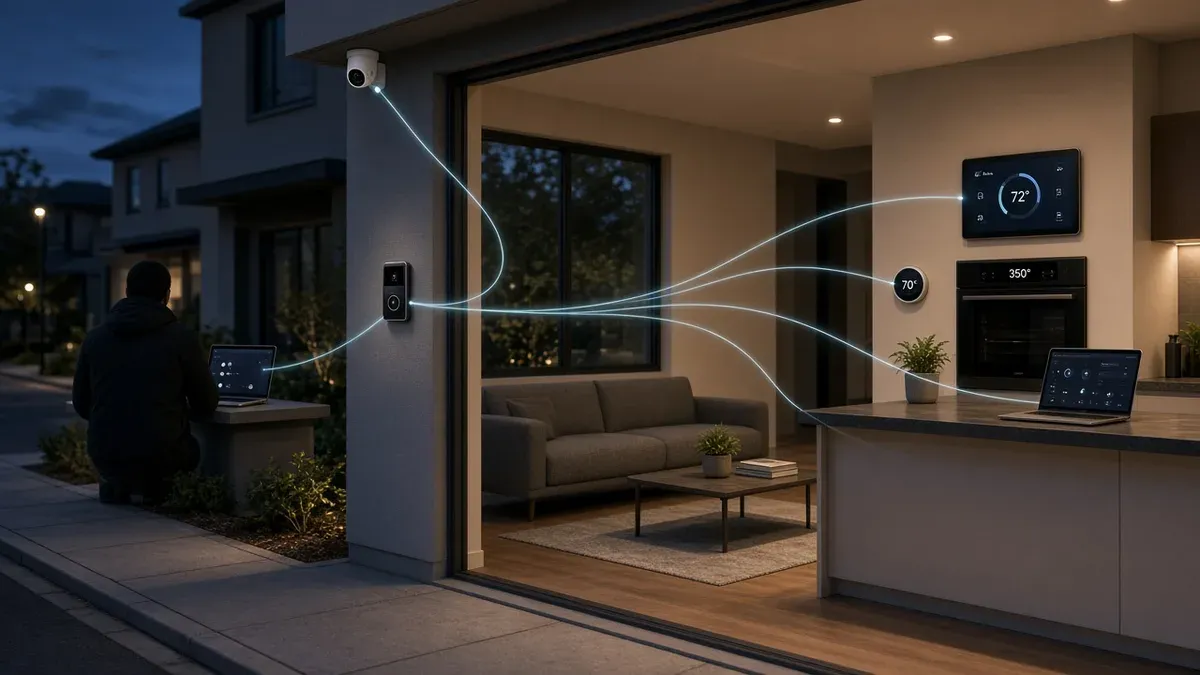
Being on the LAN enables probing and targeted attacks — not instant ownership of every gadget. - KRACK (2017). Research by Mathy Vanhoef showed that some WPA2 implementations could reinstall encryption keys during the handshake, enabling traffic manipulation or decryption on unpatched clients. Most vendors shipped fixes in 2017–2018, but forgotten IoT firmware may still be vulnerable. KRACK requires proximity; it is not the same as guessing a weak password. Primary reference: krackattacks.com · CERT VU#228519.
- No forward secrecy on PSK networks. With WPA2-Personal, anyone who knows the passphrase and has stored ciphertext can decrypt those captured frames later. WPA3-Personal (SAE) adds forward secrecy for sessions after pairing — see Wi-Fi Alliance WPA3 materials.
- Deauthentication and disassociation. Classic management frames can knock a client offline when Protected Management Frames (802.11w / PMF) are not enforced. That is an availability attack: it does not by itself decrypt video or credentials, but it can blind a camera or doorbell until it reconnects — the scenario behind many “Wi-Fi jammer” thefts. PMF and WPA3 are the practical mitigations on supported gear.
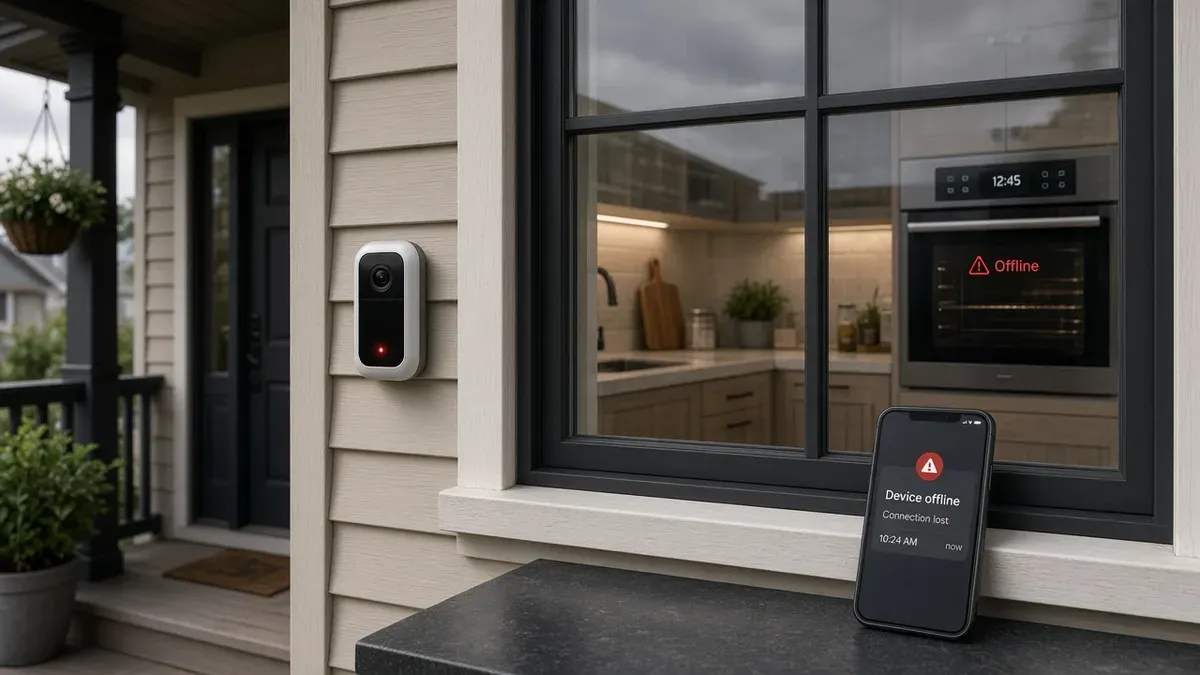
Deauth affects availability — devices may show offline even though the passphrase was never cracked. - Evil twin / rogue access points. A nearby attacker can broadcast a convincing SSID and capture credentials or push a captive portal. Mitigations include verifying router settings, using unique SSIDs, and segmenting IoT — see NIST wireless LAN guidance below.
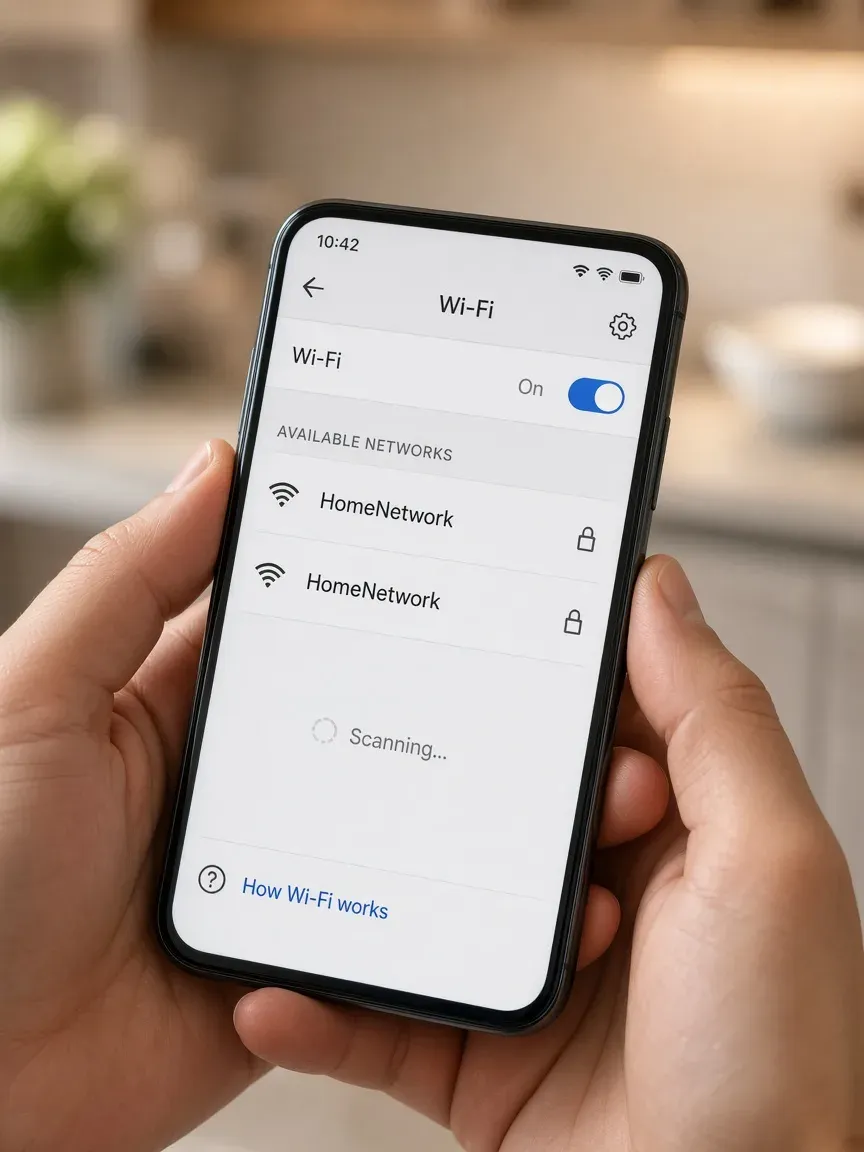
Two similar names on a phone — always confirm which AP is yours before joining.
WPA3-Personal and Enterprise
WPA3-Personal uses SAE (Simultaneous Authentication of Equals), which greatly improves resistance to offline guessing compared with WPA2’s 4-way handshake, and mandates PMF for certified WPA3 gear. Wi-Fi Alliance overview: Wi-Fi Alliance — Security · WPA3 announcement.
Dragonblood (2019). Follow-on research found implementation flaws in early WPA3 / SAE stacks (downgrade and side-channel classes). Vendors patched affected firmware; owners should still install router and IoT updates. Primary reference: Dragonblood (Vanhoef & Ronen).
What owners can do
| Priority | Action | Why it matters |
|---|---|---|
| 1 | Use a long random passphrase (or WPA3-SAE where supported) | Reduces offline PSK cracking if a handshake is ever captured |
| 2 | Install router and device firmware updates | Closes KRACK-class bugs and Dragonblood-era implementation flaws |
| 3 | Enable PMF (802.11w) — capable or required on the AP when clients allow | Hardens against forged deauth/disassoc on many WPA2 networks; mandatory under WPA3 |
| 4 | Segment IoT on a dedicated VLAN or guest SSID with firewall rules | Limits lateral movement if one gadget is compromised |
| 5 | Prefer WPA3 or WPA2/WPA3 transition only when every client supports it | Avoid WPA3-only SSIDs that brick older 2.4 GHz IoT until vendors document support |
Primary sources (verified Oct 20, 2026)
| Topic | Reference |
|---|---|
| WEP obsolescence | Wi-Fi Alliance — Security (WEP not permitted under current programs) |
| KRACK / WPA2 handshake | krackattacks.com · CERT VU#228519 |
| WPA3, SAE, PMF | Wi-Fi Alliance Security |
| Dragonblood (WPA3 implementation) | wpa3.mathyvanhoef.com |
| Wireless LAN security (rogue AP, segmentation, unauthorized access) | NIST WLAN guidelines (SP 800-153) |
| Protected Management Frames (802.11w) | IEEE 802.11w amendment; summarized in Wi-Fi Alliance security materials above |
Risk illustrations above are AI-generated scenes for education (not incident photos). Related: WPA3 upgrade checklist · Guest / IoT Wi-Fi isolation.
Incidents
| When | Topic | Source |
|---|---|---|
| Dec 2022 | Thumbnail push uploads to AWS; marketing disclosure gap | To our eufy Security Customers |
| Jun 2023 | Text-only notification default, WebRTC on web | Our Commitment to Protect You |
MFA: YubiKey and Google Authenticator
| Platform | Grade | Security key | Authenticator |
|---|---|---|---|
| Eufy Security account | Fail | Not published | No — email/SMS 6-digit codes only |
Eufy documents two-step verification via email or SMS one-time codes, not Google Authenticator–style TOTP or YubiKey enrollment (Two-Step Verification). See MFA directory.
Independent cybersecurity audits
We audited on October 20, 2026. 100% is the ideal — none reach it.
| Organization | Domain | Overall | vs 100% |
|---|---|---|---|
| Eufy | eufy.com | 57% | −43 |
| Domain | Identity | Transport | Website |
|---|---|---|---|
| eufy.com | 25% | 15% | 87% |
Audit links: eufy.com
Illustration only — scores are in the tables above.
Squat: 56 review / 0 BEC on eufy.com.
Related reading: WPA3 upgrade checklist · Devices that block WPA3-only rollouts · Guest Wi-Fi isolation.
Check your domain free at audit.emailmenow.com, or see automated reports and monitoring.
Sources: Official support articles linked in tables (last checked October 20, 2026). Independent EmailMeNow audits and scans October 20, 2026. No affiliate links.