Attackers are still hitting a critical bug in WooCommerce Wholesale Lead Capture, a paid WordPress add-on from Rymera Web Co (Wholesale Suite). BleepingComputer (September 15, 2026) and The Hacker News report that Wordfence has blocked more than 100,000 exploit attempts against CVE-2026-27540. Those counts are firewall blocks, not confirmed takeovers.
This is not a duplicate of wp2shell. That July story was WordPress Core. This one is a premium WooCommerce plugin. It is also not CVE-2026-27541 (a different Wholesale Suite privilege-escalation bug from February).
Who is at risk: stores that still run Wholesale Lead Capture 2.0.3.1 or older. Wordfence’s estimate is about 6,000 active installs. If the plugin is not on the site, this CVE does not apply.
Snapshot
| Field | Detail |
|---|---|
| CVE | CVE-2026-27540 (CWE-434 file upload) |
| Plugin | WooCommerce Wholesale Lead Capture (woocommerce-wholesale-lead-capture) |
| Affected | ≤ 2.0.3.1 · patch 2.0.3.2 (Feb 20, 2026) |
| Access | Unauthenticated upload → PHP web shell / RCE |
| CourtListener | No matching dockets as of Sept 16, 2026 |
| Stores graded | 5 vendor-named shops with public WWLC HTML — none at 100% |
Patchstack and the CVE record credit Teemu Saarentaus. Patchstack scores it 9.0. Wordfence’s write-up uses 9.8. Either way it is critical.
What the flaw does — without a how-to
Wordfence’s public description: an unauthenticated WordPress AJAX action (wwlc_file_upload_handler) trusted a client-supplied file-type allowlist. Attackers used that to drop a PHP web shell (Wordfence names shell.php as the sample they saw). The shell reported host details and offered another upload form.
We do not reprint request bodies, payloads, or attacker IP lists. Hunt from your logs and the Wordfence / BleepingComputer articles.
Wordfence said activity spiked June 4–17, July 1, and August 30, and was still lighting up the firewall in mid-September.
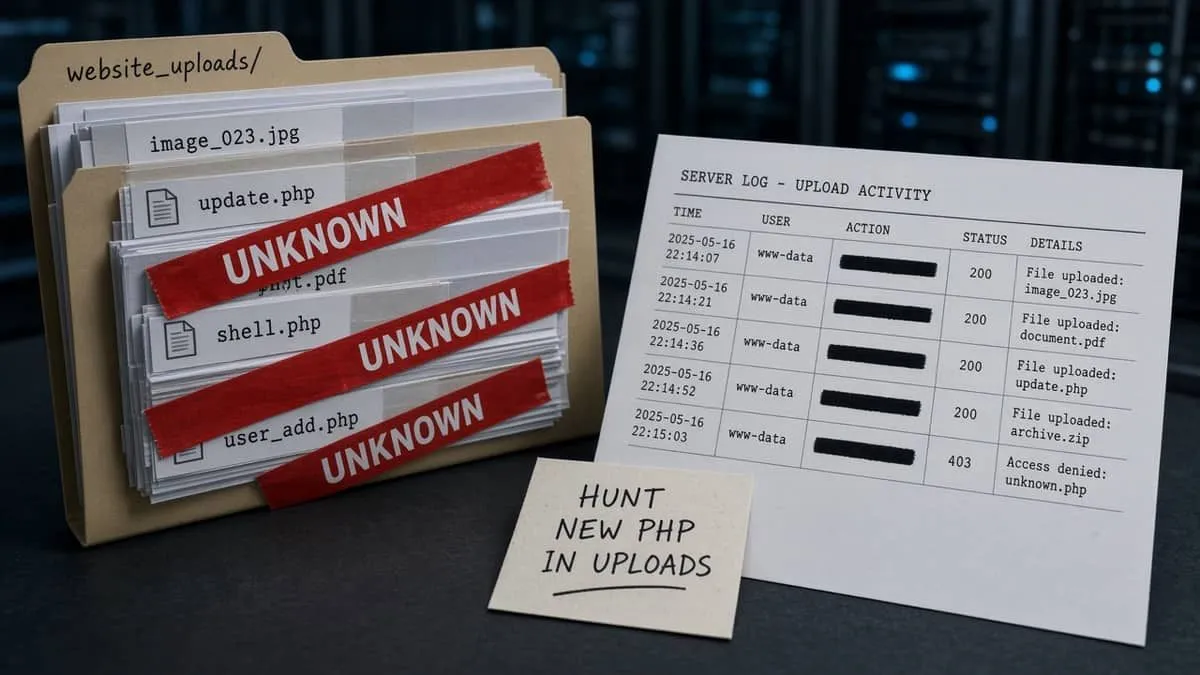
What to watch for
- New administrator (or shop-manager) accounts you did not create.
- PHP files in
wp-content/uploads(or other writeable dirs) that you did not put there — especially recent*.php. - Redirects, spam injection, checkout changes, or files that “should not be executable” in uploads.
- Web-server or WAF logs showing
admin-ajax.phpwith action wwlc_file_upload_handler.
What to do
- In Plugins, confirm whether WooCommerce Wholesale Lead Capture is installed. If it is, update to 2.0.3.2 or later from the vendor, or disable it until you can. Type wholesalesuiteplugin.com yourself — do not install a “hotfix zip” from email.
- Search uploads and plugin dirs for unexpected .php. Compare against a known-good backup.
- Review Users for unknown admins. Rotate WordPress, hosting, and WooCommerce passwords from a clean computer.
- If you confirm a shell: restore from a clean backup, then patch. Wordfence says picking persistence apart by hand is often harder than a restore.
- Put a WAF (Wordfence, Patchstack, host WAF) in front while you patch. Report crime at IC3.
A hardware key on wp-login.php does not block this upload path. It does slow the follow-on fake-admin logins after a shell.
MFA: YubiKey and Google Authenticator
This bug does not need your second factor. Grades match our MFA directory.
| Grade | Meaning |
|---|---|
| Fail | SMS, voice, or email OTP — or no public MFA path |
| Pass | Self-serve Google Authenticator-style open TOTP |
| Strong | FIDO2 / YubiKey-class security key for sign-in |
| Platform | Grade | YubiKey | Authenticator |
|---|---|---|---|
| WordPress.com | Strong | Yes | Yes |
| Wordfence Central | Pass | No | Yes |
| Wholesale Suite shop | Fail | No | No |
WordPress.com names YubiKey-class security keys, passkeys, and authenticator apps (Google Authenticator-class). WooCommerce.com store logins that use WordPress.com inherit that. Self-hosted WordPress has no built-in MFA; the official Two-Factor plugin documents Google Authenticator. A companion WebAuthn plugin adds hardware keys — that is extra software, so the self-hosted row stays Pass unless you install it.
Wordfence Central 2FA names Google Authenticator, Authy, and peers. It does not name a YubiKey enrollment path.
We found no public YubiKey or Google Authenticator docs for a Wholesale Suite customer account. Patching the plugin still comes first.
Directory: MFA support directory · Email & Identity (WordPress.com) and Business Apps (Wordfence).
Recommended MFA tools
| Product | Best for | Get it |
|---|---|---|
| YubiKey 5C NFC | USB-C laptops + NFC phones | Amazon |
| YubiKey 5 NFC | USB-A desktops + NFC phones | Amazon |
| Proton Pass | Passkeys + authenticator-style TOTP | Proton Pass |
We may earn a commission if you buy a YubiKey or sign up for Proton Pass through the links above.
Independent cybersecurity audits
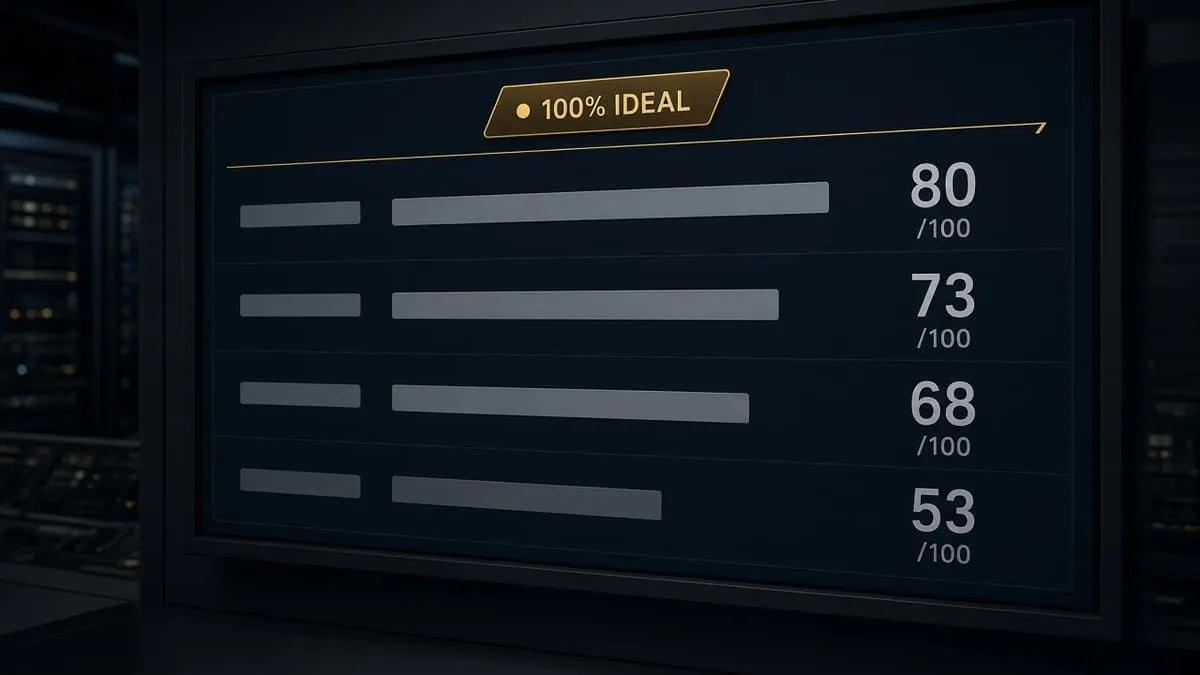
We audited official WooCommerce, WordPress.org, Wordfence, and vendor hosts on September 16, 2026. 100% is the ideal — none reach it. These scores are public email / transport / website posture. They do not score the plugin CVE.
| Organization | Domain | Overall | vs 100% |
|---|---|---|---|
| WooCommerce | woocommerce.com | 80% | −20 |
| Wordfence | wordfence.com | 73% | −27 |
| WordPress.org | wordpress.org | 68% | −32 |
| Wholesale Suite | wholesalesuiteplugin.com | 53% | −47 |
| Domain | Identity | Transport | Website |
|---|---|---|---|
| woocommerce.com | 75% | 15% | 98% |
| wordfence.com | 50% | 80% | 98% |
| wordpress.org | 90% | 15% | 37% |
| wholesalesuiteplugin.com | 50% | 15% | 42% |
Audit links: woocommerce.com · wordfence.com · wordpress.org · wholesalesuiteplugin.com
woocommerce.com at 80% is still −20 from the ideal. Transport 15% on WooCommerce, WordPress.org, and the vendor shop is a mail-transport gap — not a reason to trust a “plugin hotfix” email. Vendor HQ rymera.com.au scored 37% (not in the four-row board). Patchstack scored 50%.
Website stack note
Passive website-tech probes on September 16, 2026:
| Domain | Stack signal |
|---|---|
| woocommerce.com | WordPress on WordPress VIP; version hidden; Let’s Encrypt TLS expires 2026-12-12 |
| wordpress.org | WordPress; version hidden; Let’s Encrypt TLS expires 2026-10-23 |
| wholesalesuiteplugin.com | WordPress 7.1 (current); Google TLS expires 2026-12-06 |
| rymera.com.au | WordPress 7.0.4 (behind 7.1); Let’s Encrypt TLS expires 2026-12-08 |
| wordfence.com | Stack undetected; Amazon TLS expires 2027-03-04 |
Point-in-time only. A current vendor marketing homepage is not a finding that customer stores are patched.
Wholesale Suite shops we graded
Rymera’s marketing site names 25,000+ Wholesale Suite stores. Wordfence’s Lead Capture estimate is about 6,000. Those are different products. This CVE hits Lead Capture only.
We did not scan the internet for victims and we did not version-check readme.txt or hit admin-ajax.php. The list below is vendor case-study brands whose public HTML still shows Wholesale Lead Capture (plugin folder names, CSS handles, or WWLC shortcodes). A fingerprint is not a patched/unpatched verdict.
| Store | Domain | Public signal | Overall |
|---|---|---|---|
| Fjordpharm | fjordpharm.com | Lead Capture files | 64% |
| Kalamazoo Industries | kalamazooindustries.com | Lead Capture + Order Form | 52% |
| Strohmedico | strohmedico.com | Lead Capture files | 47% |
| Baby BeeHinds | babybeehinds.com.au | WWLC shortcode | 43% |
| My Ocean Jewellery | myoceanjewellery.com | WWLC shortcode | 36% |
100% is the ideal. These scores are email / transport / website posture. They do not score CVE-2026-27540.
| Domain | Identity | Transport | Website |
|---|---|---|---|
| fjordpharm.com | 75% | 45% | 40% |
| kalamazooindustries.com | 50% | 15% | 37% |
| strohmedico.com | 35% | 15% | 42% |
| babybeehinds.com.au | 25% | 15% | 40% |
| myoceanjewellery.com | 10% | 15% | 37% |
Audit links: fjordpharm.com · kalamazooindustries.com · strohmedico.com · babybeehinds.com.au · myoceanjewellery.com
Fjordpharm’s homepage generator names WooCommerce Wholesale Prices 2.2.7.2 (the pricing plugin). Kalamazoo’s Lead Capture / Order Form files load from kalamazooind.com (same 52% overall). Baby BeeHinds and My Ocean still publish [wwlc_…] shortcodes that the theme did not render as forms — leftover copy, or the plugin is off. Confirm in Plugins, not from this table.
Vendor case studies we could not fingerprint from public HTML: Milton & King (trade pages, no plugin folder names; miltonandking.com audited 42%), OZO Coffee (wholesale.ozocoffee.com returned 403 to our crawler), and Queen Bee Wraps (older spotlight, no current plugin paths).
Customer-store website-tech (September 16, 2026):
| Domain | Stack signal |
|---|---|
| fjordpharm.com | WordPress; generator Wholesale Prices 2.2.7.2; Let’s Encrypt TLS expires 2026-12-06 |
| strohmedico.com | WordPress 7.1; Let’s Encrypt TLS expires 2026-10-21 |
| kalamazooindustries.com | WordPress, version hidden; plugin files on kalamazooind.com; SSL.com TLS expires 2026-12-01 |
| babybeehinds.com.au | WordPress, version hidden; generator Advanced Coupons; Let’s Encrypt TLS expires 2026-11-20 |
| myoceanjewellery.com | WordPress, version hidden; PHP 8.3.25; Let’s Encrypt TLS expires 2026-10-16 |
If any of these shops (or yours) still runs Lead Capture ≤2.0.3.1, update to 2.0.3.2 or later from the vendor. Public HTML cannot replace that check.
Blacklist and lookalike domains
Email blacklist checks (public DoH, September 16, 2026): woocommerce.com, wordfence.com, wordpress.org, wholesalesuiteplugin.com, rymera.com.au, and the five graded shops (fjordpharm.com, kalamazooindustries.com, strohmedico.com, babybeehinds.com.au, myoceanjewellery.com) were clear on mail/domain lists we can query. WordPress.org web/CDN showed an informational Barracuda note; Rymera and Baby BeeHinds web/CDN showed SPFBL. Do not lead as “WordPress is blacklisted.”
DNS lookalike scans (BEC profile, registered signals only):
| Brand scanned | To review | Likely owned | BEC staging |
|---|---|---|---|
| woocommerce.com | 18 | 16 | 1 |
| wordpress.org | 45 | 25 | 0 |
| wordfence.com | 6 | 0 | 0 |
| wholesalesuiteplugin.com | 0 | 0 | 0 |
| fjordpharm.com | 2 | 0 | 0 |
| kalamazooindustries.com | 0 | 0 | 0 |
High-interest registered names (investigate; not proof this CVE used them):
| Lookalike | Technique | Note |
|---|---|---|
| woocommerces.com | insertion | BEC staging (NS + MX) |
| wocommerce.com | omission | Registered — not WooCommerce |
| wordfence.us | tld-swap | Registered — not Defiant |
| wordpress.com | tld-swap | Real Automattic product, not a fake |
| fjordpharm.net | tld-swap | Registered — not the shop we graded |
| fjordpharm.org | tld-swap | Registered — not the shop we graded |
Type woocommerce.com and the vendor plugin page yourself. Continuous monitoring: Cybersquat Domain Monitoring.
Related coverage
- wp2shell — WordPress Core unauthenticated RCE
- Google redirect trust-proxy phishing
- MFA support directory
Run a free audit at audit.emailmenow.com or contact EmailMeNow for WordPress / WooCommerce hardening, WAF, and phishing-resistant MFA aimed at the 100% ideal.
Sources: BleepingComputer (Sept 15) · The Hacker News · CVE-2026-27540 · Patchstack · Wordfence coverage via those reports and Central 2FA help · WordPress.com security keys · Two-Factor plugin · Wholesale Suite case studies. Independent EmailMeNow audits, website-tech, blacklist, cybersquat, CourtListener, and public-HTML plugin fingerprints September 16, 2026. Domain scores: audit.emailmenow.com only. Fingerprints are not patch checks. No matching RECAP/docket hits. No exploit samples.