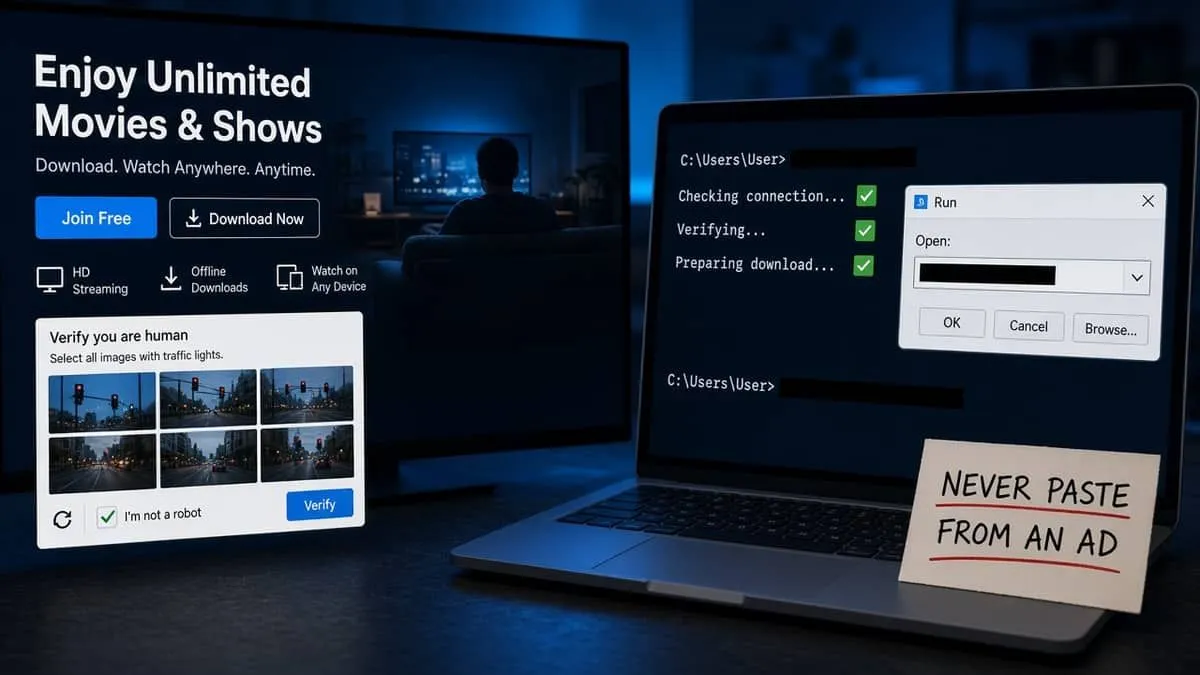
Attackers took over HBO Max’s verified Reddit account (u/hbomax) and used its trusted ad status to run a 48-hour malvertising blitz. Hudson Rock and ADAMnetworks counted 108 distinct ads. Clicking them sent Windows and Mac users to lookalike download pages that asked them to paste a command — the ClickFix pattern — then dropped infostealers, loaders, fake wallets, and crypto clippers.
This is not a reported hack of HBO Max’s streaming platform. PCMag said Warner / HBO Max had not commented as of mid-September. Reddit paused the ads and opened a security review. It is also not a duplicate of ChatGPT share-link malware (real OpenAI share URLs, not a hijacked brand account) or ClickLock Stealer (a different ClickFix locker family).
A Reddit user flagged a macOS HBO Max app ad from u/hbomax on September 6, 2026. HBO Max does not ship a native Mac app. Treat any “download HBO Max for Mac” ad as hostile.
Snapshot
| Field | Detail |
|---|---|
| What happened | Verified u/hbomax ads → ClickFix paste pages |
| Window | About 48 hours; first public report Sept 6 |
| Scale | 108 ads · 46 used an HBO Max lure |
| Max streaming | Not reported breached |
| CourtListener | No matching campaign dockets as of Sept 15, 2026 |
What the ads did
Researchers named the wider delivery system PasteSwitch: the victim pastes one command, then the kit switches payload by OS and lure. Help Net Security and The Register match Hudson Rock’s ad mix:
| Lure | Ads | Defanged landing |
|---|---|---|
| Fake HBO Max app | 46 | hbomaxx[.]app · hbomax-macos[.]com |
| Fake OpenAI Codex | 36 | codex-craft[.]com |
| Fake Mac disk utility | 15 | apple.clean-disk-guide[.]com |
| Other “dev tools” | 11 | code-desktop[.]com |
The first reporter also named hbomaxx[.]us. We do not link those hosts. Malwarebytes says some visitors saw a blank page or a redirect to a real vendor, which hid the kit from scanners.
macOS paths described by researchers used a paste-into-Terminal style drop and stealers such as MacSync and AMOS (browsers, Telegram, Notes, saved passwords, wallet seed phrases). Windows paths used a Run / PowerShell / mshta style drop toward an in-memory loader and Amatera. Clippers (AnimateClipper / ZigClipper) swap copied crypto addresses; Hudson Rock says some C2 hints sat in Binance Smart Chain contracts (36 mainnet changes March–July 2026). Those names are researcher labels, not a company attribution from Reddit or Warner.
We do not reprint commands, hashes, or live lure URLs.
Were you affected — what to do
You are in scope if you clicked a Reddit ad from u/hbomax around September 6–8 (the ~48-hour window after the first report) and followed on-screen paste / Run / Terminal steps — or installed a “Mac HBO Max app,” Codex desktop, or disk-cleaner from that ad.
- Do not paste anything a webpage copied for you. Close the tab. Do not “finish setup.”
- Stream only from the Max / HBO Max app or site you already have, or type max.com / hbomax.com yourself. There is no official native Mac HBO Max installer in an ad.
- If you already pasted or ran the prompt: take the device offline. From a clean computer, change Reddit, email, bank, and crypto-wallet passwords. Assume browser cookies and saved passwords may be gone. Rotate wallet keys if you use crypto.
- Scan with an up-to-date endpoint product. Malwarebytes says it blocks ember-bridge[.]com as PasteSwitch infrastructure — still do not visit it.
- Report at IC3 and ReportFraud.ftc.gov. On macOS Tahoe 26.4+, Apple’s Terminal paste warning helps some people — do not rely on it.
A hardware key on Reddit does not undo a command you already ran. It does cut a lot of the follow-on fake logins that show up after an infostealer.
MFA: YubiKey and Google Authenticator
ClickFix never needs your second factor. It needs you to run attacker code. Grades match our MFA directory.
| Grade | Meaning |
|---|---|
| Fail | SMS, voice, or email OTP — or no public MFA path |
| Pass | Self-serve Google Authenticator-style open TOTP |
| Strong | FIDO2 / YubiKey-class security key for sign-in |
| Platform | Grade | YubiKey | Authenticator |
|---|---|---|---|
| Pass | No | Yes | |
| HBO Max / Max | Fail | No | No |
Reddit’s 2FA help documents a 6-digit authenticator app (Google Authenticator-class). Passkeys are also documented. Public Reddit 2FA pages do not name a YubiKey enrollment path, so this row is Pass, not Strong. Brand-account 2FA still would not have stopped a session that was already stolen.
HBO Max account-security help covers unique passwords, device lists, and phishing. It does not document YubiKey or Google Authenticator. SMS appears only when adding an email to a phone-created account. That is Fail.
Directory: MFA support directory · Category → Social & Professional (Reddit) and Email & Identity (Max).
Recommended MFA tools
| Product | Best for | Get it |
|---|---|---|
| YubiKey 5C NFC | USB-C laptops + NFC phones | Amazon |
| YubiKey 5 NFC | USB-A desktops + NFC phones | Amazon |
| Proton Pass | Passkeys + authenticator-style TOTP | Proton Pass |
We may earn a commission if you buy a YubiKey or sign up for Proton Pass through the links above.
Independent cybersecurity audits
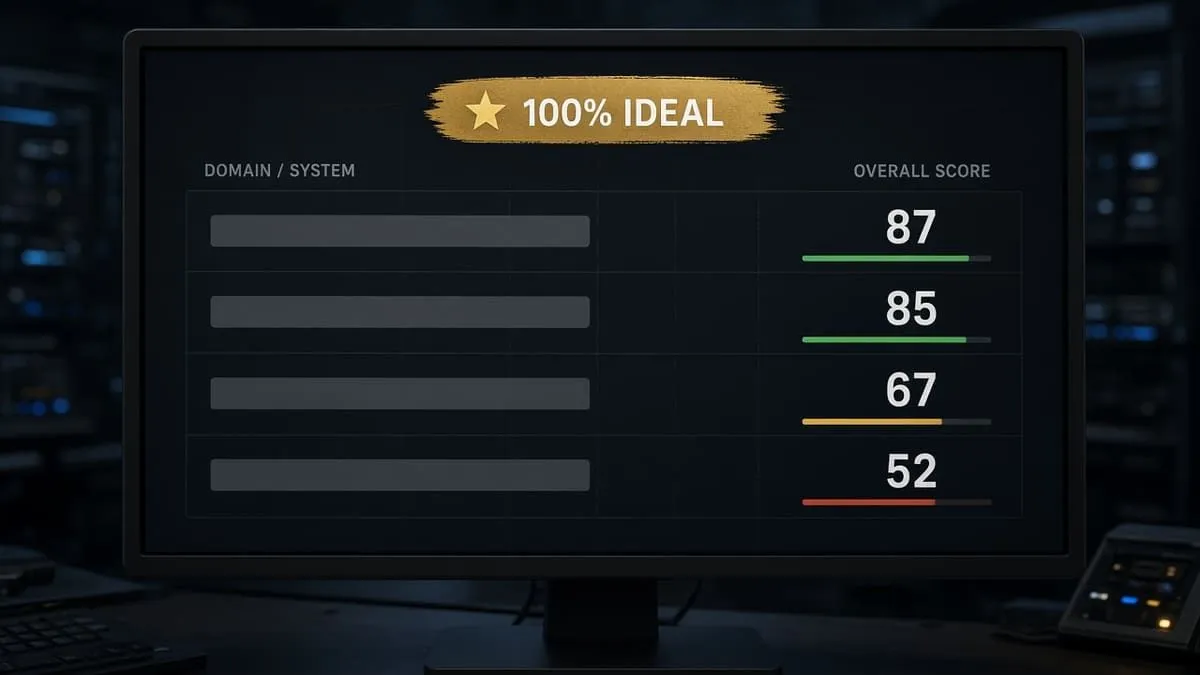
We audited official Reddit, Max, HBO Max, and reporting hosts on September 15, 2026. 100% is the ideal — none reach it. These scores are public email / transport / website posture. They do not explain how u/hbomax was taken over.
| Organization | Domain | Overall | vs 100% |
|---|---|---|---|
| FBI IC3 | ic3.gov | 87% | −13 |
| reddit.com | 85% | −15 | |
| HBO Max | hbomax.com | 67% | −33 |
| Max | max.com | 52% | −48 |
| Domain | Identity | Transport | Website |
|---|---|---|---|
| ic3.gov | 90% | 45% | 97% |
| reddit.com | 90% | 15% | 95% |
| hbomax.com | 50% | 15% | 87% |
| max.com | 50% | 15% | 37% |
Audit links: ic3.gov · reddit.com · hbomax.com · max.com
reddit.com at 85% is still −15 from the ideal. Transport 15% on Reddit and both Max hosts is a mail-transport gap — not a reason to trust a “Max desktop” ad. Parent wbd.com scored 61% (not in the four-row board). Researcher host malwarebytes.com scored 71%. ic3.gov is the reporting host.
Website stack note
Passive website-tech probes on September 15, 2026:
| Domain | Stack signal |
|---|---|
| reddit.com | Stack undetected; DigiCert TLS expires 2027-02-16 |
| max.com | Stack undetected; Amazon TLS expires 2027-03-04 |
| hbomax.com | engage-v2 (X-Powered-By); Amazon TLS expires 2027-01-03 |
| wbd.com | Drupal (version hidden); Amazon TLS expires 2027-02-23 |
| ic3.gov | Stack undetected; DigiCert TLS expires 2027-01-05 |
Point-in-time only. A live marketing homepage is not a forensic finding on the Reddit ad account.
Blacklist and lookalike domains
Email blacklist checks (public DoH, September 15, 2026): reddit.com, max.com, hbomax.com, wbd.com, and ic3.gov were clear on mail/domain lists we can query. Reddit web/CDN IPs showed informational SPFBL notes. Do not lead as “Reddit is blacklisted.”
We did not HTTP-probe malware landing pages. DNS lookalike scans (BEC profile, registered signals only) on the official brands:
| Brand scanned | To review | Likely owned | BEC staging |
|---|---|---|---|
| reddit.com | 84 | 6 | 1 |
| hbomax.com | 52 | 0 | 1 |
| max.com | 70 | 1 | 0 |
| wbd.com | 64 | 0 | 3 |
max.com is a three-letter name, so most “lookalikes” are unrelated generic brands (including mac.com). Do not treat that list as Max phishing. High-interest registered names on the HBO Max / Reddit scans (investigate; not proof this campaign used them):
| Lookalike | Technique | Note |
|---|---|---|
| hbomaxx.com | duplication | Same extra-x pattern as hbomaxx[.]app / [.]us |
| hbornax.com | homoglyph | BEC staging (NS + MX) |
| hb0max.com | homoglyph | Registered (NS + MX) |
| r3ddit.com | homoglyph | BEC staging (NS + MX) |
| w-bd.com | hyphenation | BEC staging — parent ticker host |
Type max.com or hbomax.com yourself. Continuous monitoring: Cybersquat Domain Monitoring.
Related coverage
- ChatGPT share-link malware — trusted URL, not a platform hack
- ClickLock Stealer — macOS ClickFix locker
- Google redirect trust-proxy phishing
- Chamber sites and ClickFix-style paste lures
- MFA support directory
Run a free audit at audit.emailmenow.com or contact EmailMeNow for DMARC / MTA-STS and phishing-resistant MFA aimed at the 100% ideal.
Sources: Hudson Rock — PasteSwitch / u/hbomax ads · ADAMnetworks · Malwarebytes (Sept 15) · Help Net Security · The Register · PCMag · Reddit 2FA and passkeys on signup · HBO Max account security. Independent EmailMeNow audits, website-tech, blacklist, cybersquat, and CourtListener searches September 15, 2026. Domain scores: audit.emailmenow.com only. No matching RECAP/docket hits for this campaign.